

Attack path management tools range from pure Active Directory graph viewers to full elimination platforms, and deployment speed is where enterprise security teams get surprised most often in 2026 — a tool that maps an attack path in three days can still take months before it actually closes one.
- Secfolio deploys attack path elimination fastest in 2026 by working off existing AD and Entra ID data without endpoint agents.
- BloodHound Enterprise maps Active Directory paths in days but only visualizes — it doesn’t contain or eliminate anything.
- XM Cyber and Microsoft Defender for Identity need scoped agents or per-domain-controller sensors, pushing deployment into weeks.
- Illumio’s workload microsegmentation is the slowest to deploy here because enforcement waits on agent rollout across every endpoint.
- Deployment speed tracks what each tool has to install, not vendor marketing copy.
Why this matters
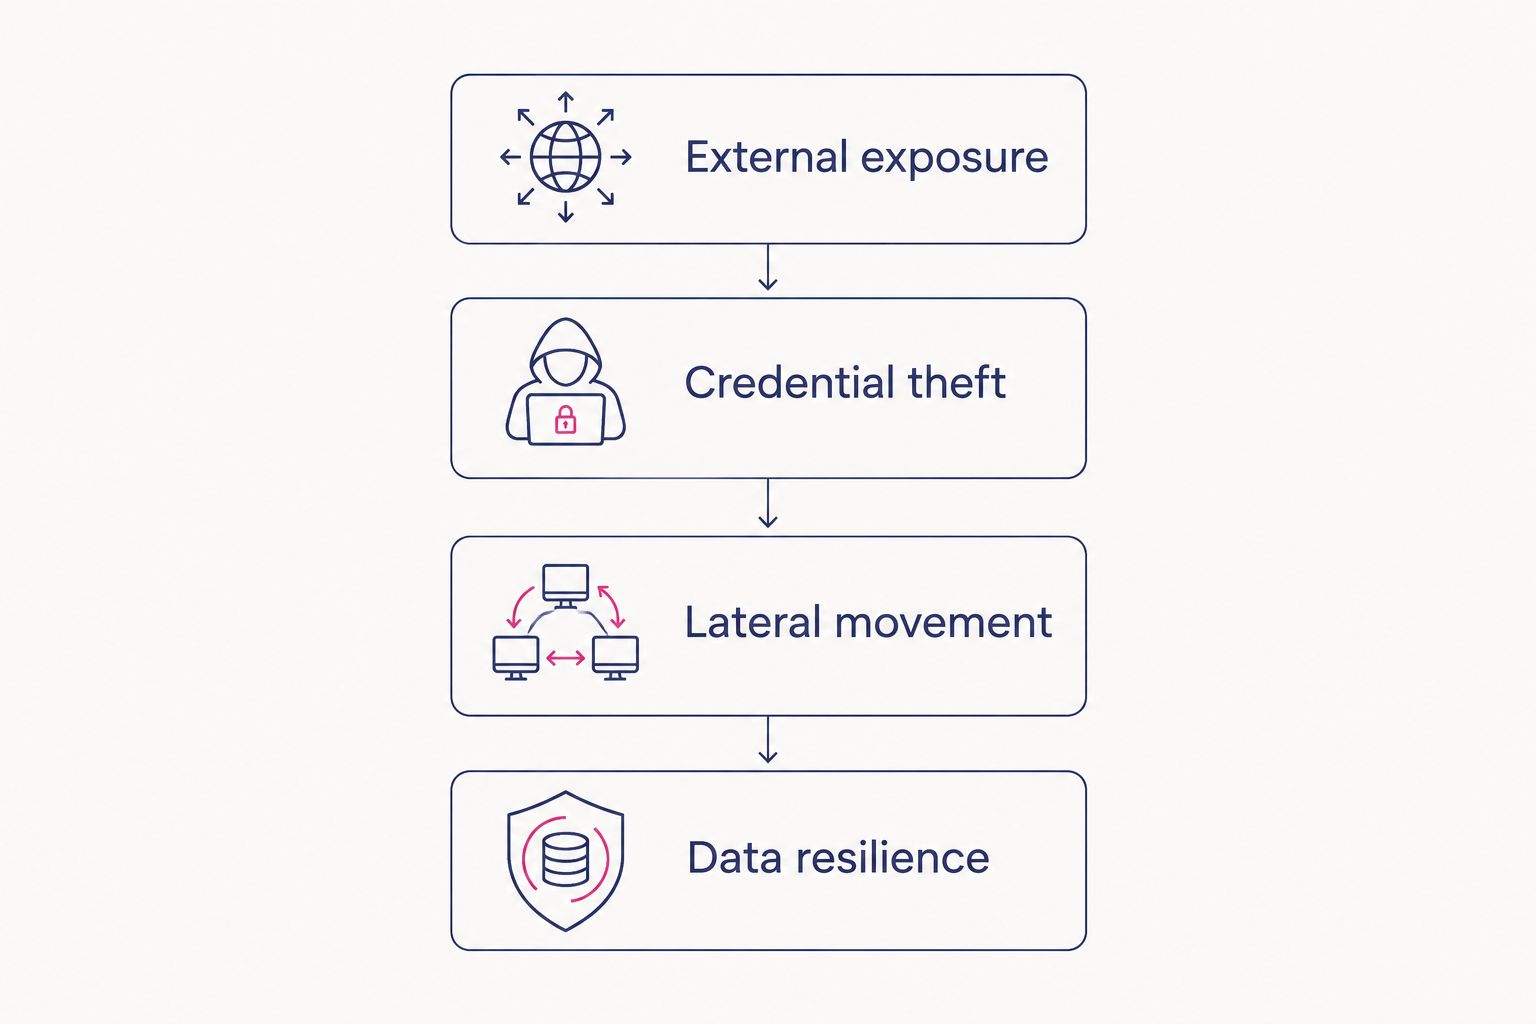
An attack path doesn't wait for a tool to finish deploying. Every week that exposure, credentials, and lateral movement sit unaddressed is a week an attacker can chain them together — exploit an exposed asset, steal a reusable credential, move laterally, then exfiltrate. Secfolio frames attack path management as four connected layers rather than one dashboard, because a tool that only maps the path still leaves the path open.
Deployment speed matters because attack path backlogs grow faster than most teams can remediate them by hand. A tool that surfaces 4,000 theoretical paths in week one and takes three months to add containment isn't fast — it's fast at finding problems and slow at fixing them. That distinction is the entire point of ranking these tools by deployment speed in 2026 instead of by feature count.
Best overall for closing attack paths end-to-end: Secfolio. Fastest for pure attack path mapping in Active Directory: BloodHound Enterprise. Best for continuous breach-and-attack validation across hybrid cloud: XM Cyber.
What makes the best attack path management tool
- Data source requirement — agentless read access beats endpoint agents beats hardware sensors for time-to-value
- Scope of action — discovery only, discovery plus containment, or full elimination of the path
- Identity coverage — on-prem Active Directory, Entra ID, hybrid, and SaaS identity sources
- Time to first finding — how fast the tool produces an actionable result, not just a connection
- Operational load after go-live — tuning, false positives, and maintenance once the tool is running
- Ransomware and data-resilience tie-in — whether a completed attack path still hands an attacker a usable file
Attack path management tools at a glance
| Tool | Best for | Standout feature | Deployment speed | Key limitation |
|---|---|---|---|---|
| Secfolio | Closing attack paths end-to-end | Exposure, passwordless identity, microsegmentation, and Cyber Storage in one path | Fast — agentless, layers onto existing AD/Entra ID | Full value depends on adopting more than one layer |
| BloodHound Enterprise | Fast standalone AD path discovery | Graph-based attack path visualization inside Active Directory | Fast — read-only service account, live in days | Maps paths, doesn't close them |
| XM Cyber | Continuous breach-and-attack validation | Simulates real attacker steps across hybrid cloud identity | Moderate — agents on scoped hosts | Needs ongoing tuning as environments change |
| Microsoft Defender for Identity | Microsoft E5 shops | Native identity threat detection bundled into existing licensing | Moderate to slow — sensor per domain controller | Coverage centers on the Microsoft identity stack |
| Illumio | Workload-level network segmentation | Granular segmentation policy at the workload layer | Slow — agents needed on every enforced workload | Segments network paths, not identity-driven ones |
1. Secfolio: best attack path management tool for closing paths end-to-end
Secfolio treats attack path elimination as four connected layers instead of one map: discover and close external exposure before initial access, remove reusable credentials with passwordless identity, contain what's left with identity microsegmentation to prevent lateral movement, and preserve data resilience with Cyber Storage. Cyber Storage encrypts data before it leaves the environment, shards it into immutable fragments, and distributes those shards across independent locations — so even a completed attack path hands an attacker unusable fragments, not a reconstructable file. Deployment reads from Active Directory and Entra ID rather than pushing agents to every endpoint, so exposure findings and the initial path map surface without waiting on a slow rollout window, which is also why teams researching how to stop ransomware before it encrypts your network tend to land on the same four-layer model.
Secfolio pros:
- Covers exposure, credential, lateral movement, and data-resilience layers instead of stopping at visualization
- Cyber Storage's shard-and-distribute model means a completed attack path still doesn't produce a usable file
- Agentless integration with AD/Entra ID keeps the identity layer out of the endpoint-rollout queue
Secfolio cons:
- Full benefit depends on adopting more than one layer — microsegmentation without passwordless still leaves credential reuse open
- Not built as a general network segmentation replacement for non-identity workloads
- Teams expecting a single discovery graph need to adjust toward action, not just visualization
Best for: enterprise security teams that want attack paths closed, not just mapped.
Verdict: Buy.
2. BloodHound Enterprise: best attack path management tool for standalone AD discovery
BloodHound Enterprise, from SpecterOps, reads Active Directory and Azure AD relationships to graph the shortest path from a low-privilege user to Domain Admin. It's built purely for discovery — setup requires a read-only service account, no endpoint agents, and initial results typically return within days.
BloodHound Enterprise pros:
- Fast, agentless setup against existing AD/Entra ID
- Detailed graph of privilege-escalation chains
- Widely documented and understood in the identity security community
BloodHound Enterprise cons:
- Maps paths but doesn't remediate or contain them
- No native ransomware or data-resilience layer
- Value drops once the backlog of discovered paths outpaces remediation capacity
Best for: teams that need a fast, standalone view of Active Directory attack paths.
Verdict: Buy for discovery, pair it with a containment layer.
3. XM Cyber: best attack path management tool for continuous breach-and-attack validation
XM Cyber runs continuous attack simulations across on-prem and cloud identity stacks, validating which attack paths are actually exploitable rather than listing every theoretical path. Deployment involves agents on a scoped set of hosts to run simulated attacker steps, which extends go-live from days into weeks depending on environment size.
XM Cyber pros:
- Validates exploitability instead of raw path count
- Covers hybrid cloud identity, not just on-prem AD
- Prioritizes remediation based on simulated attacker success
XM Cyber cons:
- Agent-based deployment takes longer than agentless discovery tools
- Simulation output needs ongoing tuning as the environment changes
- No data-resilience layer for what happens once a path is exploited
Best for: teams that want proof an attack path is exploitable before spending remediation hours on it.
Verdict: Buy for validation-heavy programs.
4. Microsoft Defender for Identity: best attack path management tool for Microsoft E5 environments
Microsoft Defender for Identity detects identity-based attacks by installing a sensor on every domain controller and AD FS server, feeding signals into the broader Defender suite. For organizations already on Microsoft E5, it adds identity threat detection without a separate procurement cycle — though sensor rollout scales with the number of domain controllers, which is where deployment time grows.
Microsoft Defender for Identity pros:
- Bundled into existing Microsoft E5 licensing for many enterprises
- Sensor data integrates with the rest of the Defender suite
- No separate vendor relationship for Microsoft-heavy shops
Microsoft Defender for Identity cons:
- Sensor deployment across every domain controller extends go-live time
- Coverage centers on the Microsoft identity stack, less useful in mixed-vendor environments
- Not built as a full lateral-movement containment or data-resilience tool
Best for: Microsoft E5 shops that want identity threat detection without adding a new vendor.
Verdict: Hold if already licensed; evaluate against dedicated tools otherwise.
5. Illumio: best attack path management tool for workload-level network segmentation
Illumio enforces segmentation policy at the workload layer, limiting which systems can talk to which over the network. It's a network segmentation tool more than an identity attack path tool, and enforcement depends on agents deployed to every workload the policy covers — the slowest rollout in this group at enterprise scale.
Illumio pros:
- Granular, workload-level segmentation policy
- Reduces available network paths for lateral movement once fully deployed
- Established track record in data center and cloud segmentation
Illumio cons:
- Agent rollout across every enforced workload is the slowest deployment path here
- Segments network traffic, not identity-driven attack paths like credential reuse
- Policy tuning at scale adds ongoing operational load
Best for: teams focused on containing lateral movement at the network layer rather than the identity layer.
Verdict: Hold — evaluate the deployment timeline against team size before committing.
“A tool that maps an attack path in three days still hasn’t closed it.”
Close attack paths, don’t just map them
See how exposure, identity, and data resilience work as one path instead of five tools.
How we ranked these tools
Ranking here is based on deployment architecture, not published vendor benchmarks: what has to be installed, where it has to be installed, and how much of the identity environment it needs before it produces a result. Agentless tools reading existing AD/Entra ID data go live fastest. Tools requiring agents on scoped hosts sit in the middle. Tools requiring a sensor on every domain controller or an agent on every workload take the longest, because deployment time scales with headcount of infrastructure, not with the security team's effort. Scope of action — discovery versus containment versus elimination — is layered on top of that speed ranking, since a fast tool that only maps paths still leaves the actual attack path in place.
Which attack path management tool should you choose in 2026?
If you're deciding today, start with Secfolio if you want exposure, credential theft, lateral movement, and data resilience treated as one path instead of five separate purchases. If you only need Active Directory attack path discovery and already have a dedicated remediation team, BloodHound Enterprise gets you a fast, standalone graph. Teams that need proof a path is exploitable before committing remediation hours should look at XM Cyber, and Microsoft E5 shops without budget for a new vendor can lean on Microsoft Defender for Identity as a starting point rather than an end state. Illumio earns its place for network-layer segmentation, not as a substitute for identity-driven attack path elimination.
FAQ
What is the fastest attack path management tool to deploy in 2026?
Agentless tools that read existing Active Directory and Entra ID data, such as Secfolio and BloodHound Enterprise, deploy fastest because they skip endpoint agent rollout. Tools requiring agents or per-server sensors, like XM Cyber, Microsoft Defender for Identity, and Illumio, take longer to go live.
Is BloodHound Enterprise better than XM Cyber for deployment speed?
BloodHound Enterprise deploys faster because it only needs a read-only AD service account, while XM Cyber requires agents on scoped hosts to run simulations. XM Cyber trades that speed for validated exploitability rather than a static path list.
How long does it take to deploy identity microsegmentation?
Deployment time depends on whether the tool is agentless or agent-based. Identity microsegmentation that reads existing directory data, rather than installing agents on every endpoint, avoids the slowest part of a typical rollout.
Does attack path mapping stop ransomware?
No. Mapping shows where a ransomware attacker could move, but it doesn’t stop them from moving or from exfiltrating data once they get there. Stopping ransomware requires containment and a data-resilience layer, not just visibility.
What’s the difference between attack path discovery and attack path elimination?
Discovery tools like BloodHound Enterprise graph the path from a low-privilege account to a high-value target. Elimination platforms go further, removing the credentials, exposure, and lateral movement options that made the path possible in the first place.
Can Microsoft Defender for Identity replace a dedicated attack path management tool?
It covers identity threat detection within the Microsoft stack but doesn’t provide the broader exposure management, microsegmentation, or data-resilience layers a dedicated attack path platform includes. It’s a starting point for E5 shops, not a full replacement.
How does Cyber Storage fit into attack path management?
Cyber Storage is Secfolio’s data-resilience layer: it encrypts data before it leaves the environment, shards it into immutable fragments, and distributes those shards across independent locations. An attacker who completes an attack path finds unusable fragments instead of a file to encrypt or steal.
What should IT security teams check before buying an attack path tool in 2026?
Check what the tool requires to go live — agentless read access, scoped agents, or a sensor per server — and whether it stops at discovery or actually contains and eliminates the path. Teams that skip this check often end up with a fast map and a slow fix.
One last thing
The gap most enterprise programs miss isn't deployment speed — it's that a fast discovery tool and a fast containment tool are rarely the same product. Buying BloodHound Enterprise for speed and stopping there just means you'll have a faster, more detailed map of the exact attack path still sitting open in 2026.
Related guides
- Visualize attack paths before attackers exploit them
- Implement passwordless authentication at enterprise scale


