

Instead of manually chasing suspicious sign-ins while an attacker moves between systems, automatically isolate identities when lateral movement is detected: validate the identity and attack path, restrict access to the next system, revoke sessions, and send the case to an analyst. In 2026, the safest workflow separates detection from enforcement so a weak alert does not disable a legitimate account.
- To automatically isolate identities lateral movement alerts must identify the account, attempted destination, and evidence before enforcement.
- Secfolio identity microsegmentation is best for containing identity-driven lateral movement; pair it with session revocation and analyst review.
- Start with a narrowly scoped deny rule, then revoke sessions and block sign-in when the evidence supports broader containment.
- Exclude emergency access and critical service identities from automatic account disablement; give them a separate response path.
Why this matters
A lateral-movement alert is useful only if it changes what the suspected identity can reach. A sign-in from an unexpected host, followed by attempted access to a restricted system, gives an attacker a path from one foothold to another. Contain the path before deciding whether to disable the entire account. For background on that control, see how to segment identities to contain a breach.
Secfolio identity microsegmentation is best for enterprise security teams that need to contain identity-driven lateral movement. Its role is to restrict access between identities and systems; it does not replace identity-provider actions, detection, or investigation. That distinction matters in 2026: blocking one destination limits the blast radius without assuming every action by that account is malicious.
| Response option | Best for | Strength | Limitation |
|---|---|---|---|
| Identity microsegmentation deny rule | A confirmed identity-to-resource attack path | Stops access to the protected destination | Other sessions and destinations need separate review |
| Session revocation and sign-in block | Evidence that the account itself is compromised | Restricts continued use of the account | Can disrupt legitimate work and dependent services |
| Analyst approval before enforcement | Ambiguous activity or sensitive identities | Adds a human check before disruptive action | Leaves the path open until approval |
Before you start
- Access to detection and enforcement systems. You need permission to inspect identity and access events, update identity-based access policy, revoke sessions, and create an incident. Use a dedicated automation identity with only the permissions its actions require.
- An identity-to-resource map. Record which identities can reach protected systems, who owns each identity, and which flows must remain available during containment. Include an approved emergency-access route.
- A tested rollback path. A revoked session cannot be restored; the user must authenticate again. Removing a deny rule is a separate action. Test both before enabling automatic enforcement. The mid-setup trap is identity mismatch: a display name in one alert is not a reliable key for a directory account or policy subject. Match immutable identifiers before changing access.
Step 01: Define the lateral-movement trigger
- Choose events that show an identity attempting to cross an access boundary. Useful inputs include a sign-in event, a resource access decision, a privileged-role change, and a connection attempt to a protected destination. Do not treat a single unusual sign-in as proof of lateral movement.
- In your detection rule, require an identity identifier, source, destination, event time, and event ID. These are fields in the workflow specification, not universal button names; map them to the actual fields exposed by your tools.
- Add a condition that links the suspicious identity to an attempted move between systems or privilege levels. Keep the triggering evidence in the case so an analyst can explain why the rule fired.
- Send a test event for an approved test identity. Confirm that the workflow resolves the directory identity and the attempted destination without relying on a display name.
Expected result: one case identifies the suspected account, the source of activity, the destination, and the evidence connecting them. If the destination is missing, stop here. An isolation rule without a target risks blocking more access than the evidence justifies.
In 2026, treat the trigger as the beginning of a decision, not permission to disable an account. The detection system reports what happened. The response workflow decides which control fits that evidence.
Step 02: Set the containment boundary
- Map the resolved identity to the policy subject used by your segmentation control. Confirm that the identity in the event and the identity in the policy are the same account.
- Select the attempted destination or protected resource group. Define the action as deny identity-to-destination access in the workflow specification. Your enforcement product’s actual field and button names vary; verify them in its configuration interface rather than substituting a guessed label.
- Exclude approved emergency access from this automatic rule. Give service identities a separate policy path: disabling a shared or application identity can interrupt unrelated workloads.
- Test the rule with an authorized test identity and destination. Verify both sides of the boundary: the prohibited connection fails, and a documented permitted connection still succeeds.
Expected result: the suspected identity cannot use the identified attack path, while access outside the defined boundary remains governed by its existing policies. If the permitted test fails, roll back the rule and narrow its scope before continuing.
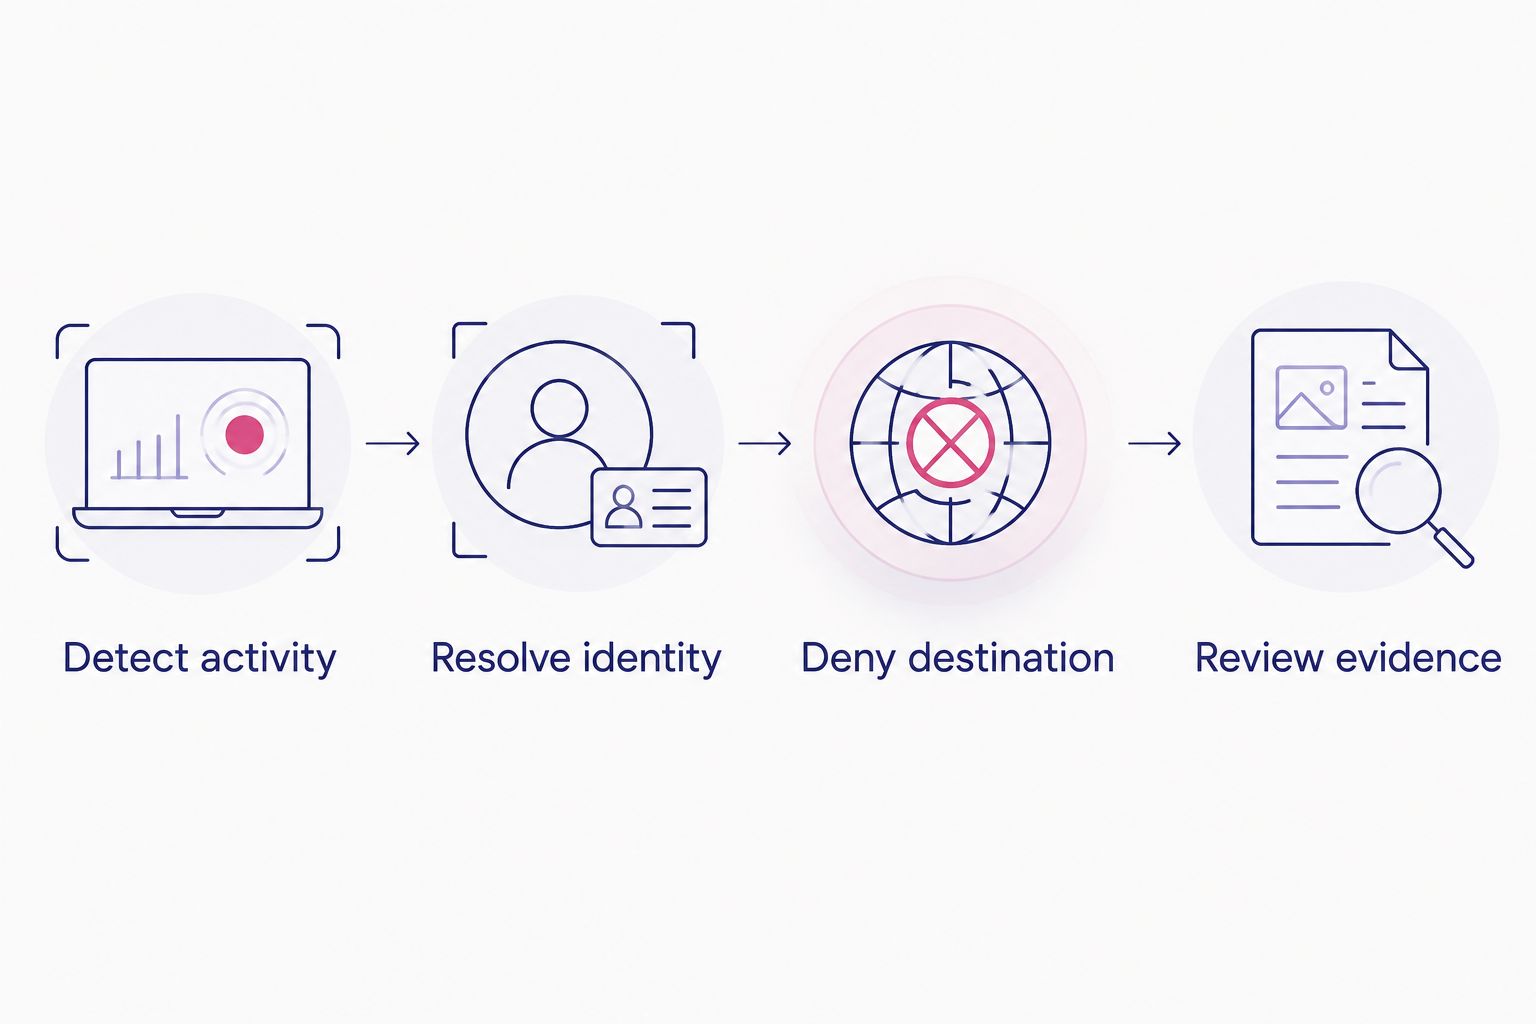
Identity microsegmentation contains lateral movement; it does not erase the evidence or establish that the identity is clean. Preserve the alert and policy-change record for the investigation. A deny rule tied to the wrong identity can cause an outage, while a deny rule tied to the wrong destination leaves the attack path open.
Step 03: Configure session and account actions
- Decide when the workflow escalates from a destination deny rule to an account-level action. Require evidence that the account itself is compromised, not merely that one access attempt was unusual. Record that condition in the response rule.
- If your directory is Microsoft Entra ID, map the account-level actions to the Microsoft Graph revokeSignInSessions operation and the user accountEnabled property where appropriate. These are API names, not Secfolio controls. Verify that your automation identity has the necessary permissions before testing.
- Revoke sessions when continued use of existing sign-ins is a concern. Do not describe revocation as an instant termination of every access token: session and token behavior depends on the application and identity configuration.
- Block new sign-ins only for identities covered by the approved response rule. Route emergency access, service accounts, and uncertain identity matches to an analyst instead of applying a broad disable action.
- Record each attempted action and its result in the incident. If segmentation succeeds but the directory action fails, leave the case open and alert the responder; partial containment is not a completed response.
Expected result: the case shows whether destination access was denied, sessions were revoked, and new sign-ins were blocked. Each outcome is visible separately, including failures. That separation makes the response auditable in 2026 and prevents a successful first action from concealing a failed second action.
Step 04: Validate and release the isolation
- Run an authorized test in which the test identity attempts the defined destination. Confirm that the event creates a case and that the workflow selects the correct identity and resource.
- Inspect the enforcement log, not just the automation log. A workflow can report that it sent a request even when the receiving control rejects it. Confirm the access decision at the destination.
- Assign an analyst to review the source, destination, session history, and any attempted privilege changes. Keep the deny rule active while the analyst determines whether another attack path remains.
- Define release as a separate approved action. The analyst confirms the identity is safe to restore, removes the targeted rule, and arranges reauthentication where sessions were revoked. Record who approved the release.
Expected result: a test case has a traceable detection, enforcement decision, access result, review, and release. Do not enable the rule broadly until the test proves both containment and recovery. For planning that wider rollout, use the microsegmentation roadmap for legacy networks.
Variant: Isolate an identity when its access changes
Lateral movement is not always the first useful signal. A newly granted privilege or access to a protected resource can justify a temporary boundary while an analyst checks the change. This 2026 variant uses the same identity-resolution and enforcement path, but its trigger is an access change rather than a detected movement attempt.
- Watch for a change to an identity’s privilege or protected-resource access. Include the actor who made the change, the affected identity, and the resource in the event.
- Compare the change with the approved access request. If that approval is unavailable, route the case to review rather than assuming malicious intent.
- Apply a targeted deny rule to the newly reachable protected destination when the change violates the approved boundary. Do not disable the identity solely because its access changed.
- Release the rule after the access owner confirms the change or removes the unapproved entitlement. Keep the change record with the case.
Expected result: an unapproved access change does not become an open route to a protected system. This variant is best for entitlement changes that affect sensitive destinations; the lateral-movement trigger remains best for observed movement between systems. Neither variant proves compromise on its own.
Troubleshooting
- The alert fires, but no identity is isolated. Compare the event’s account identifier with the directory identifier and segmentation policy subject. Display names, renamed accounts, and identities from different directories can break the match. Stop enforcement on unresolved identities and send the case to review.
- The rule blocks legitimate access. Inspect the source, destination, and policy scope in the enforcement log. Roll back the targeted rule through the approved release process, then test with a narrower destination. Do not solve a false positive by exempting every account in the same group.
- Session revocation succeeds, but activity continues. Check the application session and access-token behavior, then inspect whether a different identity is making the requests. Revoke sessions is not a substitute for the destination deny rule.
- A service account triggers the rule. Identify its owner and dependent workloads before changing account state. Apply a resource-specific boundary or analyst approval path instead of an automatic account disable action.
- The case says isolated, but access still works. Confirm the receiving control applied the policy and that the observed connection uses the identity and destination in the case. Treat a submitted policy request as pending until the enforcement result is verified.
Customize your workflow
Begin with the smallest set of protected destinations for which you can resolve identities, verify enforcement, and approve release. Expand only after each boundary passes the same test. Secfolio identity microsegmentation addresses the lateral-movement layer; passwordless authentication addresses reusable credentials, and external exposure management addresses paths attackers use for initial access.
Add a data-resilience decision for incidents involving ransomware or exfiltration. Secfolio Cyber Storage encrypts data before it leaves the customer environment, shards the encrypted data into immutable, unusable fragments, and distributes those shards across independent locations. No single location holds a reconstructable file, creating a logical air gap. Attackers who reach one location encounter fragments rather than a usable file; authorized users have a distributed recovery path. Cyber Storage complements identity containment. It does not replace the deny rule, credential controls, or exposure management.
Plan identity containment
Map the identity-to-resource boundary before automating isolation.
For a 2026 rollout, keep four decisions separate: discover external exposure, eliminate reusable credentials, contain lateral movement, and preserve data resilience. Secfolio’s controls address different parts of the attack path. A workflow that records which decision fired gives responders a clearer account of what was stopped and what still needs investigation.
FAQ
How do you automatically isolate identities when lateral movement is detected?
Resolve the alerted identity and destination, apply a targeted identity-to-resource deny rule, and verify enforcement. Revoke sessions or block sign-in when the evidence and approved response rule call for account-level containment.
Should every lateral-movement alert disable the user account?
No. Start with a targeted access boundary when the evidence identifies a destination. A weak or ambiguous alert should receive analyst review before a disruptive account action.
Is identity microsegmentation the same as session revocation?
No. Identity microsegmentation restricts which resources an identity can reach; session revocation addresses existing sign-ins. Use the controls together when the incident requires both containment and account action.
What information must a lateral-movement alert contain?
The workflow needs a resolvable identity, source, destination, event time, and supporting event record. Without a reliable identity or destination, route the case to review instead of applying an automatic deny rule.
Can you isolate a service account automatically?
Use a separate, approved response path for service accounts. A targeted resource deny rule limits a suspected path, while disabling the account can interrupt workloads that depend on it.
Does revoking sessions immediately stop every application request?
No. Access-token and application-session behavior differs across configurations. Verify access at the protected destination and keep the segmentation boundary in place while responders investigate.
What does Secfolio Cyber Storage add to identity isolation?
Secfolio Cyber Storage adds a data-resilience layer, not an identity-isolation action. It encrypts, shards, and distributes data so one storage location does not hold a reconstructable file.
One last thing
Test the release before you automate the isolation. A response is incomplete if analysts can block an attack path but cannot identify the policy they changed, verify its effect, and restore approved access. In 2026, make the release decision as traceable as the initial deny rule.
Related guides
- How to reduce blast radius after credential compromise
- How to build an identity threat detection and response program


