

Cortex XSOAR wins for large-volume enterprise SOCs. Tines wins for lean teams that want to build their own triage workflows. Torq wins for cloud-native, SaaS-heavy environments. The right pick among the best automated alert triage tools in 2026 depends on how many alerts you're drowning in and how much engineering time you have to configure a response, not just which vendor claims the fastest dashboard.
- Cortex XSOAR is the strongest automated alert triage tool for large SOCs in 2026, with a mature playbook library but a heavy setup cost.
- Tines fits lean security teams that want to build their own no-code triage workflows instead of inheriting one.
- Torq suits cloud-native, SaaS-heavy stacks chasing hyperautomation across many tools at once.
- Splunk SOAR only makes sense if Splunk is already your SIEM of record.
- A fast triage decision built on the wrong alert priority is still a wrong decision — identity context matters as much as speed.
Why this matters
An automated alert triage tool doesn't stop an attack. It decides which of the hundreds of daily alerts a human analyst sees first, and that decision determines whether a lateral-movement attempt gets contained in minutes or gets discovered three days into an incident response engagement. The seven tools ranked below all do the same core job: cut alert volume down to what actually deserves attention before an attacker finishes their objective.
Speed alone isn't the whole story. A triage engine that fires fast on the wrong alert doesn't help a SOC — it needs context about which accounts and systems actually connect to sensitive data to prioritize correctly instead of just ranking by alert count. That's the gap most AI threat triage tools comparisons skip, and it's why this ranking weighs integration depth and identity awareness alongside raw response time.
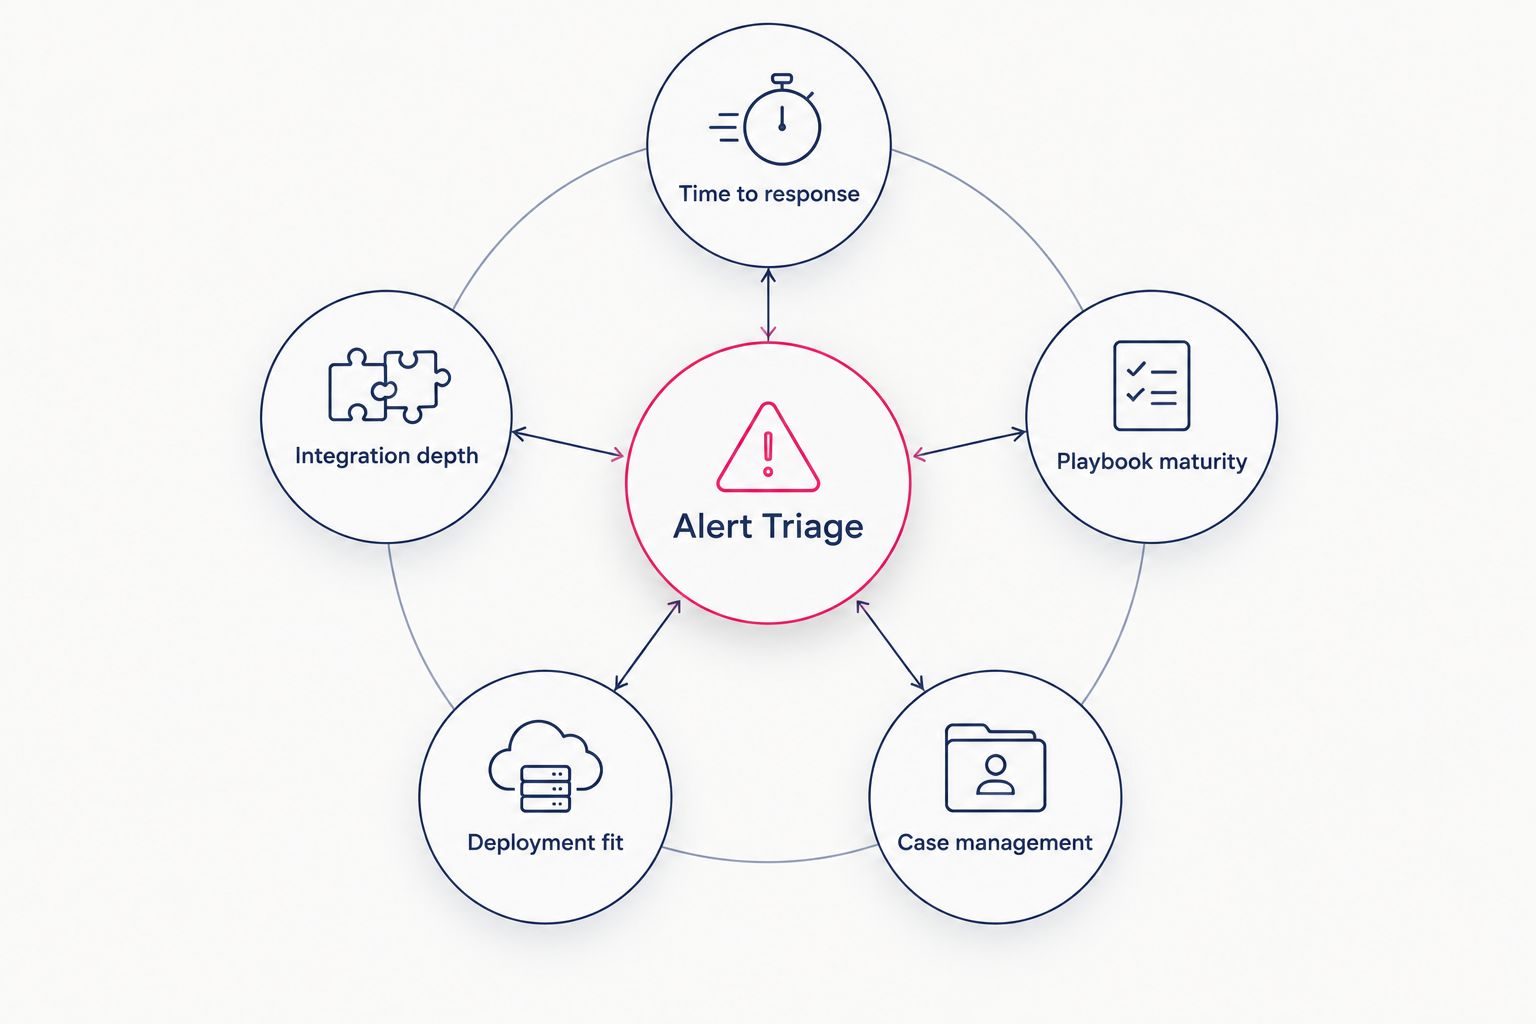
What makes the best automated alert triage tool
- Time to first response — median time from alert ingestion to an automated containment or enrichment action
- Integration depth — native connectors to EDR, identity, cloud, and network tools without custom scripting
- Playbook maturity — pre-built response workflows versus a blank canvas your team has to build
- Deployment fit — cloud-native SaaS versus on-prem or hybrid architecture matching your environment
- Case management — how well the tool documents, assigns, and closes incidents for audit and compliance
Automated alert triage tools at a glance
| Tool | Best for | Standout feature | Key limitation |
|---|---|---|---|
| Cortex XSOAR | High-volume enterprise SOCs | Large playbook and integration marketplace | Heavy setup and tuning effort |
| Splunk SOAR | Splunk-native security teams | Native fit with Splunk SIEM data | Limited value outside the Splunk stack |
| Chronicle SOAR | Google Cloud-centric stacks | Native pairing with Chronicle detections | Smaller third-party integration ecosystem |
| Microsoft Sentinel | Microsoft 365 / Azure enterprises | Deep Entra ID and Defender integration | Logic Apps learning curve |
| Tines | Lean teams building their own workflows | No-code workflow builder | Fewer pre-built playbooks |
| Torq | Cloud-native, SaaS-heavy environments | Broad SaaS connector library | Newer, smaller track record |
| Swimlane | Compliance-driven case management | Audit-ready case management depth | Heavier overhead for small teams |
1. Cortex XSOAR: best automated alert triage tool for high-volume enterprise SOCs
Cortex XSOAR, built from Palo Alto Networks' 2019 acquisition of Demisto, centralizes case management, threat intel enrichment, and playbook-driven response in one console. It's designed for teams handling thousands of alerts a day that need automation touching every one before a human does.
Cortex XSOAR pros:
- Large out-of-the-box playbook library covering common alert types
- Deep integration marketplace across SIEM, EDR, and network tools
- Built-in threat intel management alongside triage
Cortex XSOAR cons:
- Implementation and playbook tuning takes real security engineering time
- Full value depends on connecting most of your existing stack first
Best for: enterprise SOCs with dedicated automation engineers and high alert volume.
Verdict: Buy — if you have the headcount to build it out.
2. Splunk SOAR: best automated alert triage tool for teams already on Splunk
Splunk SOAR, the product formerly known as Phantom before Splunk's 2018 acquisition, plugs directly into Splunk's SIEM data model, letting analysts trigger automated playbooks from the console they already use for detection.
Splunk SOAR pros:
- Native fit for any team already running Splunk as the SIEM of record
- Visual playbook editor lowers the barrier for non-developers
- Community-contributed playbook exchange
Splunk SOAR cons:
- Value drops sharply if Splunk isn't already your primary data platform
- Licensing tied to Splunk ingestion volume complicates budgeting at scale
Best for: Splunk-native security teams that want triage automation without a second console.
Verdict: Buy if Splunk is already your SIEM, Skip otherwise.
3. Chronicle SOAR: best automated alert triage tool for Google Cloud-centric stacks
Chronicle SOAR started as Siemplify before Google's 2022 acquisition folded it into the Chronicle security suite. It's built to pair natively with Chronicle detection data and Google Cloud telemetry.
Chronicle SOAR pros:
- Tight native pairing with Chronicle detections and Google Cloud logs
- Case management built around collaborative investigation, not just automation
- Straightforward playbook builder for common response actions
Chronicle SOAR cons:
- Less mature third-party integration ecosystem outside the Google stack
- Best value requires committing to Chronicle as your detection layer too
Best for: teams standardized on Google Cloud and Chronicle for detection.
Verdict: Hold — evaluate only if Chronicle already sits under your detection stack.
4. Microsoft Sentinel: best automated alert triage tool for Microsoft-centric enterprises
Sentinel pairs cloud-native SIEM with Logic Apps-based playbooks, giving Microsoft 365 and Azure shops a triage layer inside the ecosystem where they already manage identities and endpoints.
Microsoft Sentinel pros:
- Deep native integration with Entra ID, Defender, and Azure telemetry
- Consumption-based model scales with alert volume instead of flat licensing
- Automation logic reuses skills teams already have in Azure
Microsoft Sentinel cons:
- Logic Apps has a steeper learning curve than purpose-built SOAR tools
- Multi-cloud environments get less native value outside the Microsoft stack
Best for: enterprises running Microsoft 365, Entra ID, and Defender as the core stack.
Verdict: Buy for Microsoft-heavy environments.
5. Tines: best automated alert triage tool for lean teams building their own workflows
Tines is a no-code automation builder aimed at security teams that want to design their own triage logic instead of waiting on vendor-shipped playbooks or a professional services engagement.
Tines pros:
- No-code workflow builder analysts can learn without a scripting background
- Faster to stand up a first workflow than heavier SOAR platforms
- Flexible enough to automate tasks well outside classic alert triage
Tines cons:
- Ships with fewer pre-built security playbooks than Cortex XSOAR or Splunk SOAR
- Your team designs and owns the triage logic instead of inheriting a mature library
Best for: small-to-mid security teams that want ownership over their automation logic.
Verdict: Buy for lean teams willing to build.
6. Torq: best automated alert triage tool for cloud-native, SaaS-heavy environments
Torq positions itself around hyperautomation across a sprawling SaaS and cloud toolset, connecting alert sources, identity platforms, and ticketing systems into a single automated response layer.
Torq pros:
- Broad SaaS and cloud connector library built for modern, distributed stacks
- Fast workflow authoring aimed at hyperautomation across many tools at once
- Positioned to automate beyond security into IT and DevOps alert handling
Torq cons:
- Newer entrant with a smaller long-term track record than Cortex XSOAR or Splunk SOAR
- Smaller partner and integrator ecosystem for complex custom deployments
Best for: cloud-native organizations juggling dozens of SaaS security tools.
Verdict: Hold — pilot against your specific SaaS stack before committing.
7. Swimlane: best automated alert triage tool for compliance-driven case management
Swimlane leans into low-code automation paired with case management built for teams that need to document every triage decision for audits and regulators.
Swimlane pros:
- Case management depth suited to compliance-heavy industries
- Low-code automation builder balances flexibility with usability
- Reporting built around demonstrating response process, not just speed
Swimlane cons:
- Heavier case management focus can feel like overhead for smaller teams
- Less name recognition than the major SIEM-attached SOAR players
Best for: regulated industries where audit trails matter as much as response speed.
Verdict: Buy for compliance-heavy SOCs, Skip for lean teams that don't need the overhead.
How we ranked
Each tool is scored against the five criteria above, not against a single speed benchmark. A tool with the fastest dashboard demo but a thin integration list still loses to one that connects natively to your identity, endpoint, and cloud data — because triage speed only counts once the alert has enough context to act on. Deployment fit and case management depth separated tools that look similar on a feature sheet but serve very different SOC sizes in 2026.
See identity context in your triage workflow
Attack-path context cuts false priority calls before analysts ever see them.
Which automated alert triage tool should you choose?
For most enterprise SOCs with dedicated automation staff, Cortex XSOAR is the default pick in 2026 — the playbook library and integration marketplace justify the setup cost at scale. If your team is small and wants full control over the logic, Tines is the better starting point. If your stack is Microsoft-heavy, take Sentinel; if it's cloud-native and SaaS-sprawling, pilot Torq before committing budget.
Whatever you choose, the tool is only as sharp as the context feeding it. A triage engine that treats every account and asset as equally valuable will still bury the alert that matters behind ten that don't.
FAQ
What’s the best automated alert triage tool for large SOC teams in 2026?
Cortex XSOAR is the strongest fit for large-volume enterprise SOCs in 2026, with a mature playbook library and broad integration marketplace. It requires more implementation time than lighter tools like Tines.
Is Cortex XSOAR better than Splunk SOAR for alert triage?
Cortex XSOAR generally offers a deeper standalone playbook library, but Splunk SOAR wins for teams already running Splunk as their SIEM. The better choice depends on which platform already holds your detection data.
How much does an automated alert triage tool reduce response time?
There’s no universal percentage — reduction depends on how much context an alert already carries before triage starts. Tools with deep native integrations to identity and endpoint data process alerts faster than tools that need custom connectors built first.
Can alert triage tools replace a SOC analyst?
No. Automated alert triage tools reduce the volume an analyst has to review manually, but final containment and investigation decisions on complex incidents still need a human analyst in 2026.
What’s the difference between SOAR and automated alert triage?
SOAR (security orchestration, automation, and response) is the broader platform category; automated alert triage is one function inside it, specifically the prioritization and initial enrichment step before a playbook runs.
Do automated triage tools work without identity context?
They work, but less accurately — a triage engine without identity context prioritizes by alert volume instead of by which accounts or systems are actually exposed to lateral movement.
Is Tines good enough for enterprise security teams?
Tines fits enterprise teams that want to build custom triage logic in-house, but it ships fewer pre-built security playbooks than Cortex XSOAR or Splunk SOAR out of the box.
How long does it take to deploy an automated alert triage tool?
Enterprise SOAR platforms like Cortex XSOAR typically take a security engineering team weeks to integrate properly across a full stack. No-code tools like Tines can produce a first working workflow in days.
One last thing
Most alert triage evaluations compare speed and integration count and stop there. The variable that actually predicts fewer missed incidents in 2026 is whether the tool can see identity risk — which accounts are overprivileged, which sessions look like lateral movement — before it decides an alert is low priority. A fast tool blind to that context still misses the alert that matters.
Related guides
- AI threat triage tools for security operations teams
- Security automation for SOC alert triage
- How to reduce alert fatigue for identity threat detection teams
- How to stop ransomware before it encrypts your network
- How to prevent lateral movement in enterprise networks


