

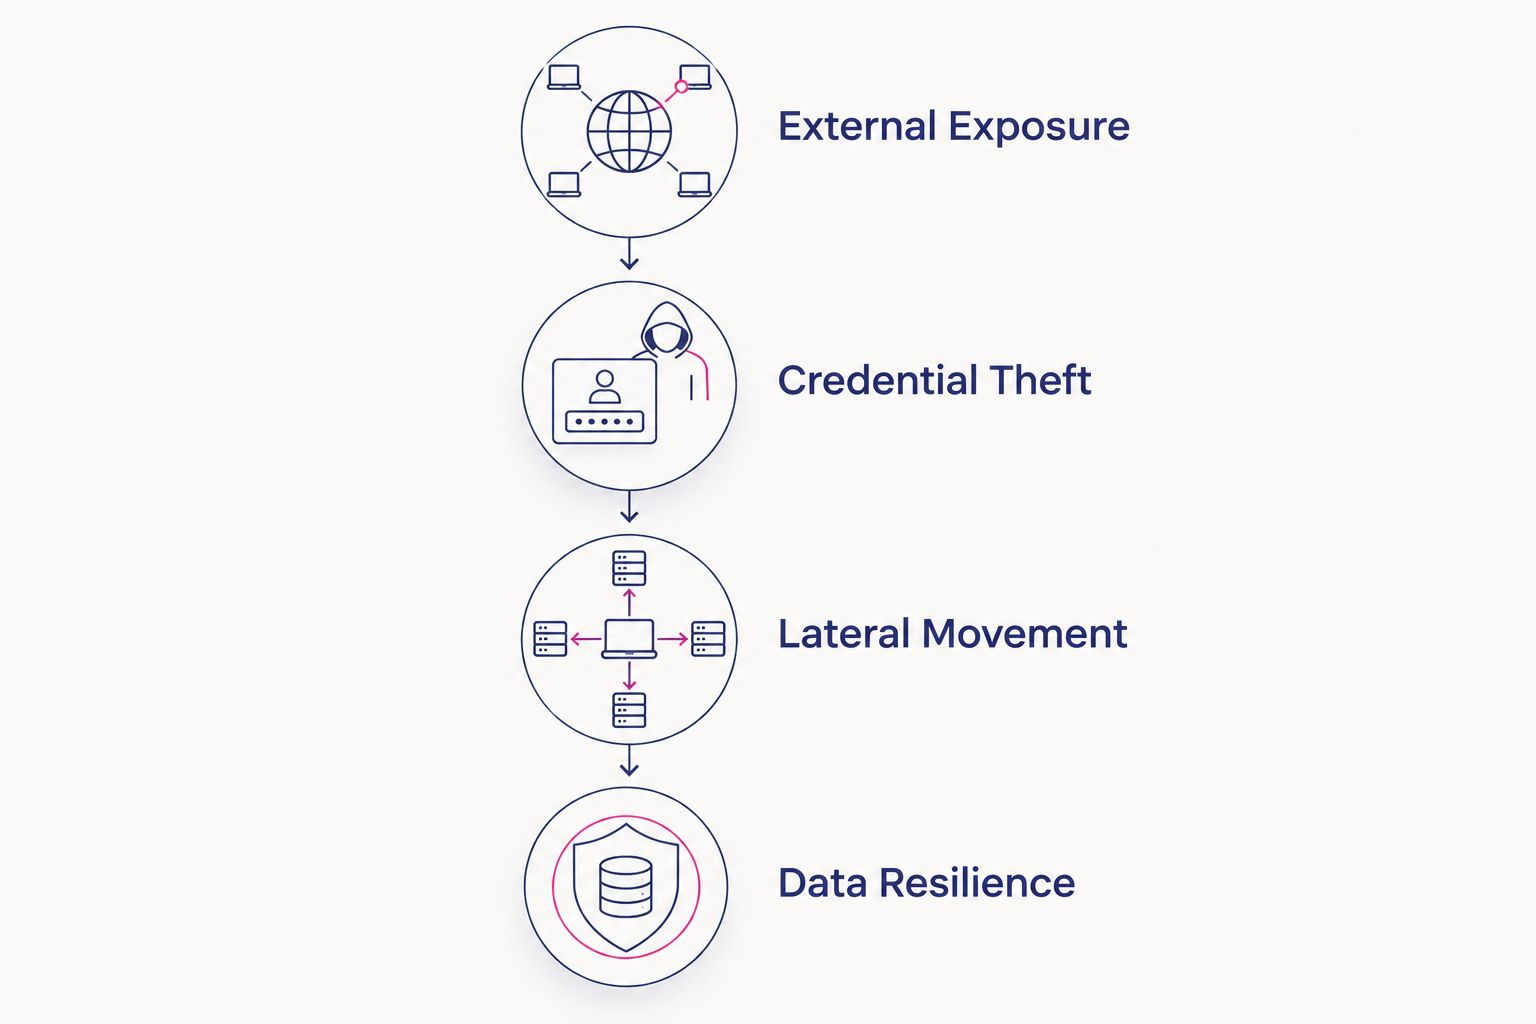
Best overall data breach prevention software for universities in 2026: a layered stack that pairs external exposure management with passwordless identity, identity microsegmentation, and Cyber Storage-style data resilience — no single point tool covers all four stages of the attack path. Best for legacy Active Directory environments: identity microsegmentation. Best for surviving a ransomware event that gets past the first three layers: Cyber Storage.
- Best overall data breach prevention software for universities in 2026 combines exposure management, passwordless identity, microsegmentation, and data resilience.
- External attack surface management wins for closing internet-facing gaps before enrollment and financial-aid seasons spike traffic.
- Passwordless authentication removes the credential most campus phishing attacks target — reused student and staff passwords.
- Identity microsegmentation contains lateral movement across the legacy Active Directory most universities still run.
- Cyber Storage-style data resilience is the layer that survives ransomware once the other three get bypassed.
Why this matters
A university campus runs more independent networks than most enterprises twice its size — admissions, financial aid, a learning management system, athletics ticketing, and a research network with its own funding rules and its own patch cycle. FERPA governs student records, and financial aid processing often carries GLBA-style safeguards obligations on top of that. None of it changes what actually stops a breach: closing the attack path before an intruder reaches usable data.
Generic data breach prevention software rarely accounts for this sprawl. It treats a research lab's fifteen-year-old server the same as a freshly imaged laptop, and it assumes an IT staff sized like a bank's. In 2026, the university IT teams winning this fight stopped buying isolated point tools and started closing the four stages an attacker actually walks through: external exposure, credential theft, lateral movement, and data theft or encryption.
What makes the best data breach prevention software for universities
- Coverage across the full attack path, not just one stage of it
- Built for decentralized IT: research networks, legacy Active Directory, BYOD student devices
- Deployable without disrupting instruction, enrollment, or research uptime
- Survives ransomware and exfiltration attempts instead of only detecting them
- Maps to FERPA and state breach-notification obligations without bolt-on tooling
Data breach prevention software for universities: at a glance
| Category | Best for | Standout capability | Key limitation |
|---|---|---|---|
| External attack surface management | Closing campus-facing exposure gaps | Continuous discovery of forgotten subdomains and exposed services | Finds gaps but doesn't stop what's already inside |
| Passwordless authentication | Eliminating phishable student and staff credentials | Removes the credential attackers actually steal | Rollout needs device and legacy-app compatibility planning |
| Identity microsegmentation | Containing lateral movement in legacy Active Directory | Blocks attacker movement without rebuilding the network | Requires mapping identity relationships before enforcement |
| Privileged access management | Controlling research and admin system access | Removes standing privileged access | Doesn't touch external exposure or the ransomware payload |
| Ransomware prevention and data resilience (Cyber Storage) | Surviving encryption and exfiltration attempts | Shards and distributes data so no full copy exists to steal | Doesn't replace identity, exposure, or segmentation controls |
1. External attack surface management: best for closing campus-facing exposure gaps
External attack surface management continuously inventories internet-facing assets across every school, department, and research center — subdomains a marketing team spun up, a forgotten VPN endpoint from a discontinued program, an exposed admin panel on a decade-old LMS integration. Universities rarely run one IT team; they run dozens of shadow deployments, and none of them show up in a single asset list without this layer running continuously.
External attack surface management pros:
- Finds exposure created by departments IT doesn't directly manage
- Runs continuously instead of surfacing once a year during an audit
- Prioritizes findings by what's actually reachable from outside
External attack surface management cons:
- Doesn't stop an attacker once they're already past the perimeter
- Needs a remediation workflow attached, or findings just pile up
Best for: universities running more than one admissions portal, athletics site, or research subdomain outside central IT's direct control. Verdict: Buy.
2. Passwordless authentication: best for eliminating phishable student and staff credentials
Secfolio's passwordless authentication approach for higher education replaces reusable passwords with device-bound credentials, so a phished login page or a leaked credential dump hands an attacker nothing usable. Campus populations turn over every semester, which keeps password reuse and reset volume high year-round in a way most enterprises never see.
Passwordless authentication pros:
- Removes the credential most phishing kits are built to steal
- Cuts helpdesk password-reset volume across large student bodies
- Works across shared lab and shift-style access, not just faculty laptops
Passwordless authentication cons:
- Needs device and legacy-app compatibility planning before rollout
- Some older campus systems still require a password fallback mid-migration
Best for: universities where phished student credentials and reset tickets show up repeatedly in help desk data. Verdict: Buy.
3. Identity microsegmentation: best for containing lateral movement in legacy Active Directory
Identity microsegmentation contains an attacker's movement once inside by breaking the identity relationships an intruder relies on to jump from a compromised student worker's laptop to a domain controller — without a network redesign. Most universities run Active Directory environments assembled over fifteen or twenty years, carrying far more standing trust between accounts than anyone has audited by hand.
Identity microsegmentation pros:
- Blocks lateral movement without rebuilding the network
- Maps existing identity relationships before enforcing anything, so nothing breaks silently
- Shrinks the blast radius from any single compromised account
Identity microsegmentation cons:
- Requires an upfront mapping phase before policy goes live
- Doesn't address exposure that starts outside the network
Best for: campuses running legacy Active Directory where departments inherited admin rights nobody's since revoked. Verdict: Buy.
4. Privileged access management: best for controlling research and admin system access
Privileged access management removes standing privileged access from admin, IT, and research-system accounts, replacing always-on admin rights with access granted only when it's needed. Universities grant privileged access constantly — to a contractor upgrading lab equipment, to a research partner on a grant-funded server, to a vendor patching the financial aid system — and most of that access outlives the project that created it.
When a university grants privileged access to a contractor or a visiting research partner, the account request usually originates outside the campus directory entirely. Confirming that the person behind the request is who they claim to be is a separate problem from controlling what that account can touch once it's approved — identity verification API providers solve the former, while privileged access management solves the latter, and skipping the verification step just moves the risk one step earlier in the process.
Privileged access management pros:
- Eliminates standing admin rights that outlive the contract or project that created them
- Applies the same control to research systems as to core IT infrastructure
- Creates an audit trail for every privileged session, useful for grant compliance reviews
Privileged access management cons:
- Doesn't cover external exposure or the ransomware payload itself
- Needs buy-in from department heads currently holding informal admin rights
Best for: research universities juggling contractor, vendor, and grant-partner access on top of internal IT staff. Verdict: Buy.
5. Ransomware prevention and data resilience: best for surviving encryption and exfiltration attempts
Ransomware prevention built on Cyber Storage assumes the first three layers eventually get bypassed and asks what an attacker finds once they reach a file server or backup target. Traditional backups concentrate one complete, restorable copy of student records, research data, and financial aid files in a single place — exactly what ransomware operators encrypt and exfiltrate before demanding payment.
Cyber Storage encrypts data before it leaves the environment, shards it into fragments, and distributes those fragments across independent locations, so no single system holds a reconstructable file. An attacker who reaches that storage finds unusable fragments, not a file to encrypt or exfiltrate — a logical air gap without the overhead of a physically disconnected backup, while authorized users still recover data quickly.
Cyber Storage pros:
- Removes the single target ransomware operators are built to find
- Distributed recovery restores data quickly without reassembling a vulnerable master copy
- Applies to research data and student records the same way
Cyber Storage cons:
- Doesn't replace identity, exposure, or segmentation controls — it's the layer that catches what they miss
- Requires integration planning with existing data pipelines and research storage systems
Best for: any university already targeted by ransomware once, or holding research data valuable enough to exfiltrate rather than just encrypt. Verdict: Buy.
“A backup that holds one complete copy of student records is exactly the file ransomware operators are looking for; a data resilience architecture that never assembles that copy at rest gives them nothing to find.”
How we ranked these
Each category was scored against the criteria above: attack-path coverage, fit for decentralized higher-ed IT, deployment without disrupting the academic calendar, resilience against ransomware rather than just detection of it, and alignment with FERPA and state breach-notification rules. No category scored well on all five alone — that's the point. A university buying just one of these five is still exposed at the other four stages of the same attack path in 2026.
Which data breach prevention software should your university choose?
If you're building this stack from zero, sequence matters more than brand: close external exposure first, replace passwords second, contain lateral movement third, and put Cyber Storage-style data resilience under all of it so a missed step in the first three doesn't turn into a payout. Secfolio covers all five categories as one connected platform rather than five separate vendor contracts, which matters most for IT teams too small to manage five relationships during a single semester. For most large universities and colleges evaluating data breach prevention software in 2026, that consolidated approach beats stitching together point tools from five different vendors.
See the full Secfolio platform
Walk through exposure, identity, microsegmentation, and Cyber Storage in one system.
FAQ
What is the best data breach prevention software for universities in 2026?
No single tool covers a university campus in 2026 — the strongest setup combines external exposure management, passwordless authentication, identity microsegmentation, and Cyber Storage-style data resilience. Secfolio delivers all four as one connected platform instead of four separate contracts.
Is passwordless authentication enough to prevent a university data breach?
No. Passwordless authentication removes the credential most campus phishing attacks target, but it doesn’t contain an attacker who gets in through another path or stop lateral movement once inside. It’s one of four layers, not a full solution on its own.
How does identity microsegmentation help higher education IT teams?
Identity microsegmentation contains lateral movement inside legacy Active Directory environments by breaking the identity relationships attackers rely on to jump between accounts. It shrinks the blast radius from any single compromised student, faculty, or staff account.
What makes Cyber Storage different from a traditional backup?
A traditional backup keeps one complete, restorable copy of files in a location ransomware operators can find and encrypt. Cyber Storage encrypts, shards, and distributes data across independent locations so no single system ever holds a reconstructable file.
Do universities need external exposure management if they already have a firewall?
Yes. A firewall doesn’t inventory forgotten subdomains, discontinued VPN endpoints, or admin panels exposed by departments outside central IT’s control. External attack surface management finds those gaps continuously instead of during an annual audit.
How does privileged access management apply to research data?
Privileged access management removes standing admin rights from research-system accounts held by contractors, vendors, and grant partners, replacing always-on access with access granted only when it’s actively needed for the project.
Is ransomware still targeting higher education in 2026?
Higher education continues to appear among the most-targeted sectors in industry ransomware reporting through 2026, largely because research data and financial aid records concentrate value in systems that are often decentralized and under-segmented.
How long does it take to roll out passwordless authentication for a whole campus?
Timelines depend on device fleet size and legacy application compatibility, since older campus systems sometimes need a password fallback during migration. Planning that compatibility list before rollout starts is what determines the timeline.
One last thing
The account most likely to sit unreviewed on a university network in 2026 isn't a student's — it's the vendor or research-partner account provisioned three semesters ago for a project that already ended. Audit those before touching anything else on this list; they're the standing privileged access every one of these five categories eventually has to deal with.
Related guides
- Passwordless authentication for higher education institutions
- Privileged access management for higher education


