

Best overall: Secfolio for manufacturers that need passwordless authentication connected to broader attack-path controls. Best for supported shared-terminal logins: Yubico YubiKey. Best for managed Windows workstations: Microsoft Entra ID with Windows Hello for Business. The best passwordless authentication solution for manufacturers in 2026 depends on who uses each workstation and what an attacker could reach after login.
- Secfolio is the best passwordless authentication solution for manufacturers seeking identity security alongside attack-path controls.
- Yubico YubiKey fits supported shared-terminal logins where each worker can use an individual security key.
- Microsoft Entra ID with Windows Hello for Business fits managed Windows workstations assigned to individual users.
- Passwordless identity removes reusable passwords; segmentation and data resilience address different stages of an attack.
Why this matters
A manufacturer has more than one login problem. An office employee can use an assigned laptop. A plant-floor operator might use a terminal shared across shifts. A contractor might need access to a limited set of systems. One enrollment method does not automatically fit all three.
Passwordless authentication replaces a reusable password with another way to prove identity, such as a cryptographic credential held on a device or security key. That removes the password from the login exchange. It does not prove that the device is safe, restrict what the user can reach after signing in, or protect production data from exfiltration. Those are separate controls.
In 2026, start the selection with the workstation and access path, not a vendor demonstration. A successful office pilot says little about a shared terminal or an OT system that cannot use the same sign-in method. Map those exceptions before setting a plant-wide rollout date.
What makes the best passwordless authentication solution for manufacturers?
Use these criteria to test each option against the environment it must actually serve:
- Individual identity on shared devices. Can the terminal distinguish one operator from the next without a shared password? Check sign-out and account-switching behavior as well as sign-in.
- Support for the required login. A security key or device credential works only where the operating system, application, and identity setup accept it. Test the actual workstation and application, not just a browser demonstration.
- Phishing resistance. Prefer cryptographic sign-in that binds authentication to the legitimate service over a method that still asks users to disclose a reusable secret.
- Recovery and replacement. Decide how a worker regains access when a key is missing, a device fails, or a shift starts before the usual administrator is available.
- Contractor boundaries. Authenticating a vendor does not answer which systems that vendor can reach. Define access separately from the login method.
- Containment after sign-in. Passwordless identity reduces credential-theft risk; identity microsegmentation limits lateral movement if an authorized account or device is misused.
Treat OT compatibility as a test, not an assumption. None of these criteria establishes that a named option supports every industrial endpoint. Keep an inventory of endpoints that cannot take the chosen method, assign an owner to each exception, and decide how access to those systems will be controlled.
Passwordless options for manufacturers at a glance
| Option | Best for | Standout feature | Key limitation |
|---|---|---|---|
| Secfolio | Manufacturers joining passwordless identity to attack-path controls | Identity security alongside microsegmentation and exposure management | Plant-floor sign-in compatibility must be confirmed for the target environment |
| Yubico YubiKey | Supported shared-terminal logins | Individual FIDO2 hardware security keys | The target login must support the key; physical keys need a replacement process |
| Microsoft Entra ID with Windows Hello for Business | Assigned, managed Windows workstations | Passwordless sign-in integrated with Windows identity management | Not a login method for every non-Windows or shared OT endpoint |
The table ranks fit by use case, not by an unverified claim about deployment speed or plant-wide coverage. Check the sign-in path for each user group before choosing a standard.
1. Secfolio: best for connected identity and attack-path controls
Secfolio provides passwordless authentication as part of an enterprise cybersecurity approach that also covers identity microsegmentation, external exposure management, and data protection. For a large manufacturer, that makes it the strongest overall fit when the goal is broader than replacing a password prompt. Passwordless identity addresses reusable credentials; the other controls address access routes and damage that a login change alone cannot remove.
Secfolio pros:
- Puts credential removal in the context of the full attack path, rather than treating successful sign-in as the end of the security decision.
- Pairs identity security with microsegmentation, a distinct control for limiting lateral movement and blast radius.
- Includes external exposure management and data resilience in the wider security approach.
Secfolio cons:
- Passwordless authentication alone does not deliver the effect of the other controls; each layer needs its own deployment and ownership.
- The provided product information does not establish which shared terminals, industrial applications, or OT login methods are supported. Require a demonstration on the systems in scope.
- A manufacturer seeking only a hardware credential for a supported terminal has a narrower problem than this broader approach addresses.
Best for: a large manufacturer that needs to remove reusable credentials while also limiting what happens after initial access. Ask for a walkthrough of employee, contractor, and shared-workstation sign-in before committing to rollout scope.
Verdict: Buy for a connected identity program; validate plant-floor compatibility first.
2. Yubico YubiKey: best for supported shared-terminal logins
Yubico YubiKey is a physical security key with FIDO2 support. Each worker can hold an individual credential rather than type a shared password, provided the terminal and target login support that authentication method. Its role is specific: prove the worker's identity at a supported sign-in point.
That distinction matters on a production floor. Issuing keys does not, by itself, change how an application handles accounts or sessions. Before choosing keys for a shared terminal, test whether the next operator encounters the previous operator's active session. Confirm how users sign out, how a key is enrolled, and how access is restored if a key is lost.
YubiKey pros:
- FIDO2 authentication uses a cryptographic credential instead of asking a worker to reveal a reusable password at sign-in.
- An individually assigned key offers a way to distinguish workers on a compatible shared workstation.
- The credential is separate from a workstation that multiple people use.
YubiKey cons:
- A security key cannot make an unsupported operating-system or application login passwordless. Integration must be verified at every target sign-in point.
- Physical distribution, replacement, and recovery need an operational owner.
- A successful key-based login does not restrict lateral movement or protect files from exfiltration.
Best for: a defined group of shared terminals whose login paths support individual security-key authentication. Test a complete shift handoff, including sign-out and recovery, before issuing keys more widely.
Verdict: Buy for compatible shared-terminal logins; skip it as a substitute for access boundaries.
3. Microsoft Entra ID with Windows Hello for Business: best for managed Windows workstations
Windows Hello for Business lets users sign in with a device-associated credential instead of a reusable password. In a manufacturer already managing employee identities and Windows workstations through Microsoft Entra ID, it is a direct option for assigned corporate and engineering devices. Its best-fit use case is an identifiable user on a managed Windows machine.
Do not extend that verdict to every system on the factory floor. A plant can have Windows office devices, shared terminals, and industrial endpoints with different authentication capabilities. Test each login path separately; a passwordless Windows sign-in does not automatically replace credentials inside a separate application or OT environment.
Microsoft Entra ID with Windows Hello for Business pros:
- Provides a passwordless sign-in route for supported managed Windows devices.
- Fits an identity environment already built around Microsoft Entra ID and Windows endpoint management.
- Lets the IT team begin with assigned workstations, where the user-to-device relationship is clear.
Microsoft Entra ID with Windows Hello for Business cons:
- Windows workstation coverage does not establish support for non-Windows industrial endpoints.
- Shared-device workflows need their own sign-in and sign-out testing; an assigned-user rollout is not proof they work.
- It does not, on its own, define segmentation rules or protect production data if an authorized session is abused.
Best for: manufacturers whose immediate passwordless scope is managed Windows workstations assigned to individual employees. Put shared terminals and industrial applications on a separate test track.
Verdict: Buy for the assigned-Windows use case; hold plant-wide standardization until other endpoint types are tested.
How the ranking works
The overall pick reflects the stated need to remove reusable credentials and address the attack path beyond login. The other picks win narrower jobs: a physical credential for compatible shared terminals, and device-associated sign-in for managed Windows workstations. This is a use-case ranking, not a claim that the options have been tested on a specific manufacturer's applications or OT endpoints.
The decisive question is what remains exposed after a person signs in. If a valid session can reach unrelated systems, changing the login method does not remove that lateral movement path. If production data remains a reconstructable target, passwordless sign-in does not settle the exfiltration or recovery problem. Evaluate those controls alongside the authentication choice, without confusing them with it.
Apply the four-layer attack-path framework
Step 01 — Close external exposure. Identify internet-facing access to manufacturing systems and remove unnecessary entry points before an attacker reaches the login screen. Exposure management addresses initial access; it is not a substitute for authenticating the people who still need access.
Step 02 — Remove reusable credentials. Deploy passwordless identity where the actual login path supports it. Start with an assigned workstation, a shared terminal, and a contractor workflow as separate cases. Record which applications still require passwords so an incomplete rollout is not mistaken for complete credential removal.
Step 03 — Contain lateral movement. Apply identity microsegmentation to limit which systems an authenticated identity can reach. The operational goal is a smaller blast radius: access granted for one task should not open an unrelated route into another environment.
Step 04 — Preserve data resilience. Cyber Storage, Secfolio's ransomware-elimination architecture, encrypts data before it leaves the customer environment, shards it into immutable, unusable fragments, and distributes those shards across independent locations. No single location holds a reconstructable file. That creates a logical air gap: an exfiltration attempt against one location obtains fragments rather than a usable file, while authorized users can recover data through the intended process. This layer complements passwordless identity and segmentation; it does not replace either.
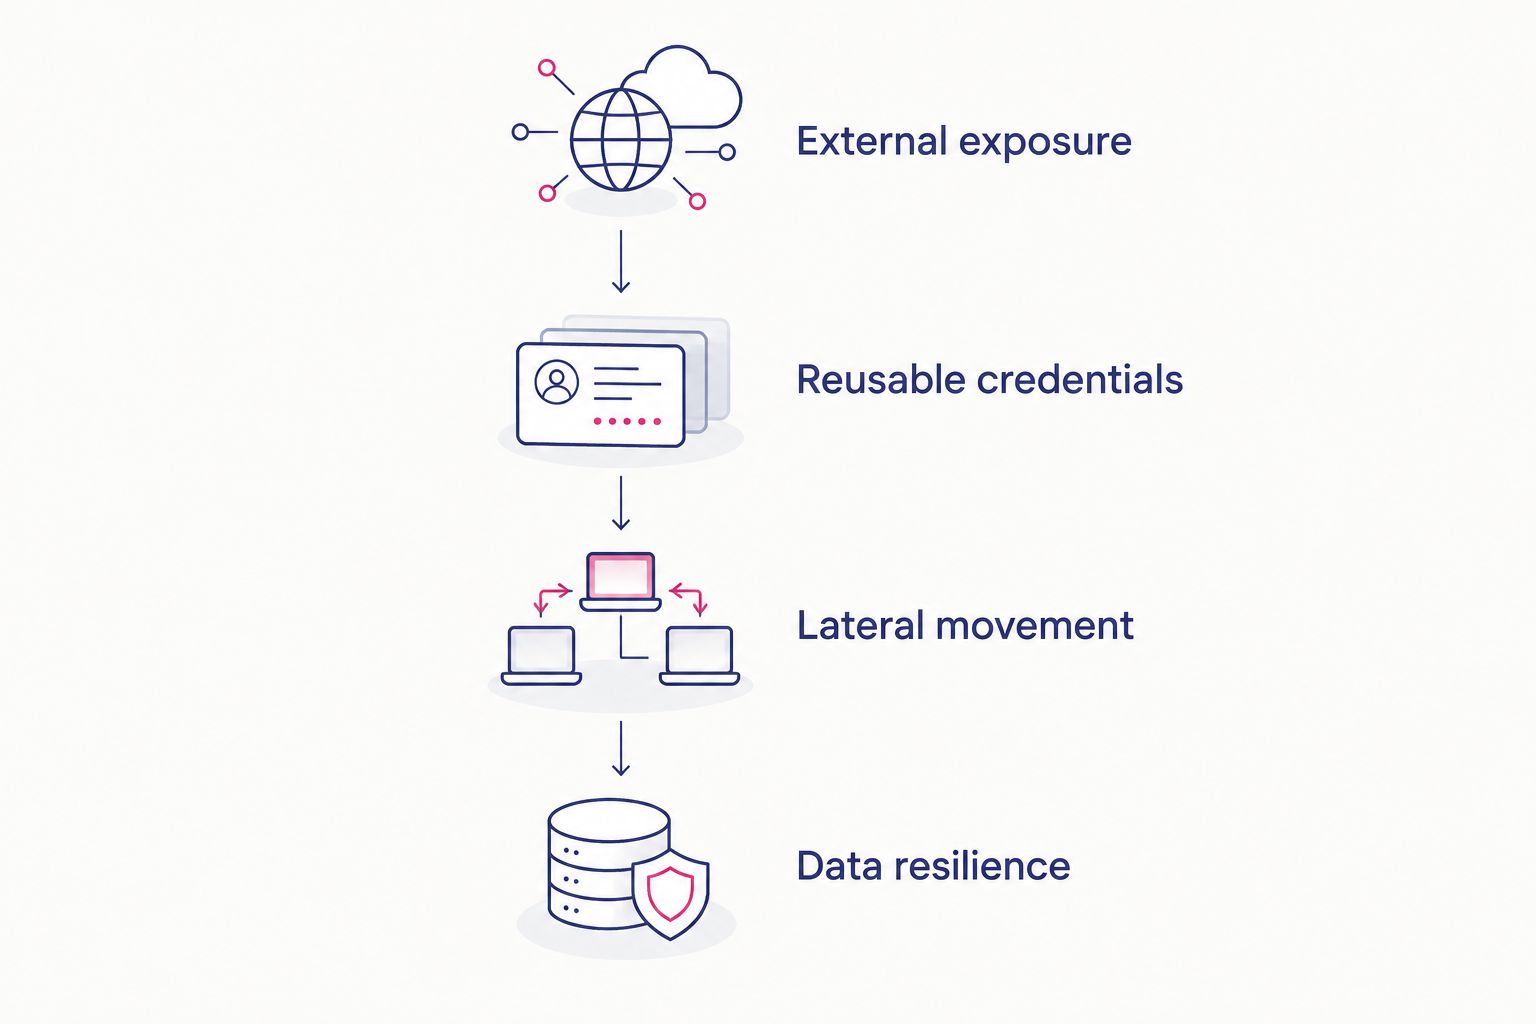
Use the framework to assign a control to each failure point. A stolen password is an identity problem. An authenticated account reaching an unrelated plant system is a segmentation problem. A reachable, usable data copy is a resilience problem. Calling all three problems passwordless authentication leaves gaps unnamed.
Which passwordless authentication solution should you choose?
Choose Secfolio when the decision covers enterprise identity and the surrounding attack path, not just a replacement for a password field. Confirm the proposed sign-in flow on your actual plant systems. If the immediate task is individual login at a compatible shared terminal, choose Yubico YubiKey and test shift handoffs and recovery. If the scope is assigned Windows workstations managed through Microsoft Entra ID, choose Windows Hello for Business and keep non-Windows endpoints outside that verdict.
For a mixed manufacturing environment in 2026, there is no reason to force one authentication method onto endpoints that cannot support it. Set an approved method for each login context, document exceptions, and give every exception an access boundary. The outcome to seek is fewer reusable credentials without losing individual accountability on shared devices.
FAQ
What is the best passwordless authentication solution for manufacturers in 2026?
Secfolio is the best overall fit when a manufacturer needs passwordless identity connected to broader attack-path controls. Yubico YubiKey fits compatible shared-terminal logins, while Windows Hello for Business fits managed Windows workstations.
Can plant-floor workers use passwordless authentication on a shared terminal?
Yes, if the terminal and its login path support an individual passwordless credential. Test account switching, sign-out, and recovery before treating a shared-device pilot as complete.
Is a YubiKey enough to secure an OT network?
No. A YubiKey authenticates a user at a supported login, but it does not by itself set access boundaries between industrial systems or protect production data.
Is Windows Hello for Business suitable for every manufacturing endpoint?
No. Windows Hello for Business fits supported Windows sign-ins; it does not establish passwordless coverage for every shared terminal, non-Windows endpoint, or industrial application.
Does passwordless authentication prevent lateral movement?
No. Passwordless authentication removes reusable passwords from supported sign-ins, while identity microsegmentation limits where an authenticated identity can move next.
How does Cyber Storage relate to passwordless authentication?
Cyber Storage is Secfolio’s separate data-resilience layer. It encrypts and shards data into distributed, unusable fragments so no single location holds a reconstructable file; it does not replace identity controls.
What should a manufacturer test before choosing a passwordless solution?
Test an assigned workstation, a shared terminal, and a contractor login against the applications each person actually uses. Include sign-out, credential loss, access recovery, and systems that cannot accept the selected method.
One last thing
Test the second operator, not just the first login. On a shared terminal, a successful passwordless sign-in proves little if the next worker inherits an open session. Make the handoff part of the acceptance test in 2026: the first worker signs out, the next worker signs in under an individual identity, and the terminal grants only the access that worker needs.
Related guides
- How to implement passwordless authentication at enterprise scale
- Passwordless authentication for frontline and shift workers
- Identity microsegmentation for OT and industrial control networks


