

Yes, passwordless authentication can be hacked or bypassed through compromised devices, stolen sessions, weak account recovery, or vulnerable applications. Correctly implemented FIDO2 authentication resists credential phishing, but it does not secure everything that happens after sign-in. This 2026 guide separates attacks against the authenticator from attacks against the surrounding system.
- Can passwordless authentication be hacked? Yes: endpoint compromise, session theft, and weak recovery remain attack paths.
- FIDO2 passkeys resist credential phishing by binding authentication to the legitimate service.
- Secfolio pairs passwordless authentication with exposure management, identity microsegmentation, and data resilience for enterprise security teams.
- Remove weak fallback methods and restrict post-authentication access; a secure sign-in alone does not prevent exfiltration.
Can passwordless authentication be hacked?
Yes. Passwordless authentication removes a reusable password, not every route into an account. The security outcome depends on the authentication method, device protection, recovery process, and permissions granted after authentication.
Start by distinguishing phishing-resistant public-key authentication from methods that merely avoid a password field. An emailed sign-in link and a FIDO2 passkey are both passwordless experiences, but they do not provide equivalent protection.
For rollout planning, use the enterprise passwordless authentication implementation guide to connect sign-in controls with enrollment, recovery, and application coverage.
| Authentication option | Best for | Security advantage | Limitation to address |
|---|---|---|---|
| Device-bound FIDO2 authenticator | Privileged access requiring a non-synced credential | Public-key authentication bound to the legitimate service | Device loss, replacement, and recovery need controlled procedures |
| Synced passkey | Users who need authentication across supported devices | Phishing-resistant authentication with credential synchronization | Protection also depends on the synchronization account and its recovery process |
| Email sign-in link | Access tied to a protected mailbox | Removes the application's reusable password | Mailbox compromise or interception of a usable link threatens access |
| SMS sign-in code | Access where stronger methods are not supported | Avoids a reusable application password | Codes are phishable; phone-number takeover is another exposure |
The W3C Web Authentication specification describes origin-bound public-key authentication. FIDO2 combines 2 protocol components: WebAuthn for the application-facing authentication flow and CTAP for communication with external authenticators. Neither component replaces application authorization or session security.
Why this matters
A successful sign-in is not proof that every subsequent action is safe. An attacker using a stolen session operates after the authentication check, while an attacker abusing recovery changes who can pass that check.
For your 2026 security review, separate 3 security boundaries: authentication, session management, and authorization. Authentication verifies the sign-in; session management carries that access forward; authorization determines which resources and actions the account can use.
Evaluate the complete attack path, not just the login screen. A phishing-resistant credential loses much of its practical value when a help desk can replace it using weak identity checks or an application still accepts a password through another route.
FIDO2 passkeys: resistant to phishing, not endpoint compromise
FIDO2 authentication uses a private key to answer a challenge from the service. The service verifies the response with the corresponding public key rather than receiving a reusable secret that an attacker can collect and replay.
The authenticator checks the service identity through relying-party and origin restrictions. A lookalike website cannot simply obtain a valid authentication response for the legitimate service through an ordinary WebAuthn ceremony.
That protection has a defined scope. Malware on an authorized endpoint can target browser sessions, manipulate application interactions, or access data available to the signed-in user without extracting the passkey itself.
Best for: enterprise accounts where credential phishing is a material attack path. Require phishing-resistant authentication for sensitive access, then protect the endpoint and limit what an authenticated account can reach.
Do not equate possession of a device with unlimited access. Local user verification, device controls, and application policy remain separate decisions that your security team must enforce.
Synced passkeys: include the synchronization account in scope
Synced passkeys retain phishing-resistant authentication at the destination service. Their distinguishing feature is that credential material is synchronized through a supporting ecosystem rather than remaining only on the original device.
This changes the operational boundary. Your assessment must include access to the synchronization account, enrollment of additional devices, and recovery of that account—not only the enterprise application's sign-in policy.
Best for: users who need supported cross-device access without relying exclusively on a single authenticator. The benefit is simpler continuity across devices; the constraint is an additional account and recovery system to assess.
For privileged roles, decide explicitly whether synchronized credentials meet your requirements. Do not infer credential storage, export behavior, or enterprise control from the word passkey alone; check the implementation you intend to deploy.
Email links and SMS codes: passwordless does not mean phishing-resistant
Email links and SMS codes remove the need to type a reusable application password. They still depend on a delivery channel and a sign-in artifact that an attacker can intercept, steal, or persuade a user to disclose.
A compromised mailbox threatens email-based sign-in. SMS authentication adds phone-number takeover risk, and a fraudulent website can ask the user to submit a valid code.
Best for: constrained access scenarios where stronger authentication is unavailable and the residual risk is acceptable. Do not recommend either method as equivalent to FIDO2 for privileged enterprise access.
For a 2026 migration, document every exception. A stronger primary method does not close the attack path if the same account retains a weaker recovery or fallback route.
Why passwordless security varies
The label passwordless describes the user experience. These implementation factors determine the actual security boundary:
- Authentication protocol: origin-bound public-key authentication protects against credential phishing differently from emailed links or delivered codes.
- Endpoint integrity: a compromised device exposes activity and sessions available to the legitimate user.
- Recovery strength: weak identity verification can let an attacker register a replacement authenticator.
- Fallback coverage: legacy passwords and weaker methods preserve alternate routes into an otherwise protected account.
- Session controls: token handling, revocation, and reauthentication determine how stolen sessions are contained.
- Authorization scope: excessive permissions increase the blast radius after any successful access.
Use these factors as acceptance criteria, not as a vendor feature checklist. Ask the application owner to demonstrate the failure case and the control that stops it.
Which attack paths remain after passwordless sign-in?
Stolen browser sessions
A session cookie or bearer token represents access that has already been granted. Where the application accepts that artifact without additional binding or checks, stealing it can let an attacker bypass a fresh authentication ceremony.
Require secure token handling and a tested revocation process. For sensitive actions, use appropriate reauthentication rather than treating an earlier successful login as permanent approval.
Fraudulent authenticator enrollment
An attacker who gains access to enrollment can register an authenticator under the victim's account. Future sign-ins then use a valid credential that belongs to the attacker.
Protect initial enrollment and later credential additions. Notify users of changes, record the event, and require stronger verification for sensitive accounts.
Weak recovery and help-desk resets
Recovery can become an alternate authentication system. If a caller can persuade support staff to reset the account using easily obtained personal information, the cryptographic strength of the original authenticator does not resolve that weakness.
Give support staff a documented verification process and escalation path. Recovery should restore legitimate access without silently lowering the account's security requirements.
Legacy and non-human access
A passwordless workforce rollout does not automatically remove service-account passwords, application secrets, API keys, or older authentication protocols. These credentials create separate attack paths.
Inventory them separately. Restrict permissions and manage their lifecycle rather than assuming a user authentication change has secured machine access.
How do you harden passwordless authentication?
Use this 2026 validation sequence before treating the rollout as complete. Each step needs evidence from the deployed environment, not a screenshot of an enabled policy.
Step 01: Require phishing resistance
Identify the accounts and applications that require origin-bound public-key authentication. Verify the actual sign-in flow and confirm that users cannot substitute a weaker method where policy prohibits it.
Name the exceptions. An unsupported application is an unresolved exposure, not proof that the whole environment is passwordless.
Step 02: Protect enrollment
Define who can add, replace, or remove an authenticator. Require verified identity and record changes so your security team can investigate unexpected enrollment.
Test a fraudulent registration attempt. The useful result is a blocked unauthorized change and an observable event.
Step 03: Harden recovery
Review lost-device handling, help-desk resets, and emergency access. Confirm that the recovery process does not introduce an unmonitored password or weaker sign-in method.
Test the process with account owners and support staff. A policy that depends on improvised verification is not a controlled recovery path.
Step 04: Secure sessions
Verify logout, administrative revocation, device-loss response, and sensitive-action reauthentication. Check application behavior rather than assuming the identity provider controls every downstream session.
Document where sessions persist independently. Those applications need their own containment procedures.
Step 05: Restrict access
Remove unnecessary permissions and constrain access between resources. An authenticated user should reach only the systems and data required for the task.
Test whether a compromised low-privilege account can reach administrative functions. This reveals the difference between secure sign-in and controlled lateral movement.
Step 06: Exercise containment
Run a controlled scenario involving a stolen session or unauthorized authenticator registration. Verify detection, session revocation, credential removal, and the restriction of downstream access.
Measure recovery against your own operational requirements. Do not substitute an assumed response time for an observed result.
Where passwordless fits in the enterprise attack-path framework
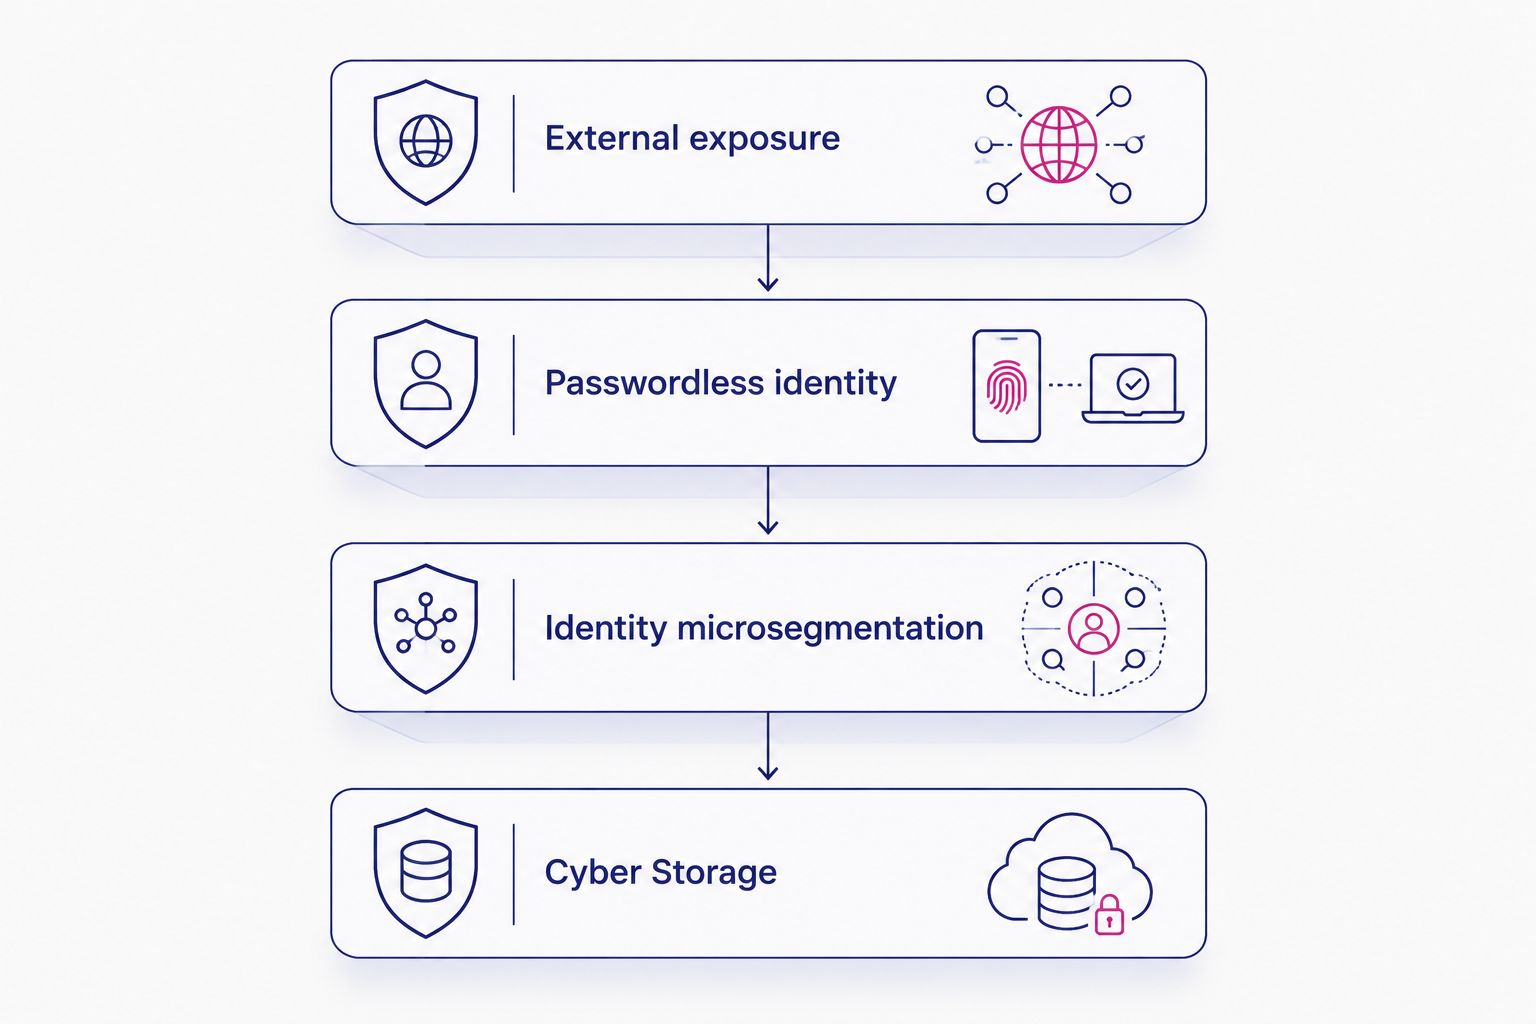
Secfolio is best suited to enterprise security teams seeking passwordless authentication within a layered attack-path defense. Its framework connects the sign-in control to exposure reduction, lateral movement containment, and data resilience rather than treating authentication as the entire defense.
The Secfolio passwordless authentication approach occupies the identity layer. The framework contains 4 control layers, each addressing a different part of an attack path:
- External exposure: discover and close exposed entry points before initial access.
- Passwordless identity: eliminate reusable passwords from protected user authentication flows.
- Identity microsegmentation: contain lateral movement and restrict the blast radius of compromised access.
- Cyber Storage: preserve data resilience through encryption, sharding, and distribution across independent locations.
The strength is separation of responsibilities. The limitation is equally clear: passwordless authentication does not replace endpoint protection, session controls, recovery verification, or application authorization.
For ransomware and exfiltration scenarios, Secfolio Cyber Storage adds a complementary data-resilience architecture. It encrypts data before it leaves the customer environment, shards encrypted data into immutable fragments, and distributes those fragments across independent locations.
No single location holds a reconstructable file. This creates a logical air gap: access to an individual storage location yields unusable digital fragments rather than complete files, while authorized recovery reconstructs the data through the architecture's recovery process.
That design does not make an authorized endpoint harmless. Applications still need usable data, so protect reconstruction access, keys, permissions, and endpoint activity; retain identity microsegmentation and exposure controls alongside distributed recovery.
Is passwordless authentication safer than passwords?
FIDO2 passwordless authentication is safer against credential phishing and password reuse. Its public-key flow removes the shared password that an attacker would otherwise steal from the user or obtain from another breach.
That verdict does not apply equally to every passwordless method. Evaluate email links, SMS codes, and recovery processes according to their own attack paths.
Can an attacker bypass a passkey without stealing it?
Yes. An attacker can target a valid session, account recovery, or a compromised endpoint without extracting the passkey. The authenticator can remain intact while another part of the access system fails.
Your incident response plan must therefore cover session revocation and unauthorized enrollment, not only credential replacement.
Does passwordless authentication stop ransomware?
Passwordless authentication blocks a reusable-password attack path; it does not stop every ransomware route. Exposed software, compromised sessions, excessive privileges, and accessible data remain separate concerns.
Use the authentication layer alongside exposure management, identity microsegmentation, and data resilience. For your 2026 review, verify each boundary independently.
FAQ
Can passwordless authentication be hacked?
Yes. Compromised endpoints, stolen sessions, weak recovery, and application vulnerabilities can bypass or undermine passwordless access without breaking the authenticator’s cryptography.
Are passkeys immune to phishing?
Correctly implemented FIDO2 passkeys resist credential phishing through service-bound public-key authentication. That protection does not prevent every social-engineering attack, including attempts to manipulate account recovery.
Can someone use a stolen device to sign in with my passkey?
A stolen device does not automatically grant passkey access when effective local user verification is enforced. Report the loss, remove unauthorized access, and revoke relevant sessions through your organization’s procedures.
Is an SMS code as secure as a FIDO2 passkey?
No. SMS codes are phishable and depend on control of the phone number, while FIDO2 passkeys use origin-bound public-key authentication.
Does changing my passkey end a stolen session?
Changing a passkey does not necessarily end an existing application session. Revoke sessions explicitly and verify how each application handles credential changes.
Do we still need identity microsegmentation after going passwordless?
Yes. Identity microsegmentation restricts lateral movement and blast radius after access is compromised; passwordless authentication addresses the sign-in boundary.
Where does Secfolio Cyber Storage fit after passwordless deployment?
Secfolio Cyber Storage adds data resilience alongside passwordless identity. Encryption, sharding, and distribution prevent a single storage location from holding a reconstructable file; they do not replace session security or access controls.
One last thing
Test the route around the authenticator before testing the authenticator itself. Ask whether a stolen session still works, whether support can enroll a replacement credential, and whether a legacy application accepts a password.
The most useful passwordless acceptance test is not another successful sign-in. It is an unsuccessful attempt to bypass the controls surrounding that sign-in.


