

Enterprise security resilience is defined as an organization’s ability to anticipate, absorb, adapt to, and rapidly recover from cyber disruptions while maintaining critical operations. The term is closely related to the industry standard concept of “cyber resilience,” which frameworks like NIST formalize as a discipline that goes well beyond traditional cybersecurity defense. For IT professionals and security managers, understanding what enterprise security resilience means in practice is the difference between surviving a breach and being crippled by one. This guide covers the core frameworks, implementation steps, and leadership factors that determine whether your organization bends or breaks under pressure.
What is enterprise security resilience, and how does it differ from traditional cybersecurity?
Enterprise security resilience and traditional cybersecurity share the same starting point but diverge sharply in their goals. Traditional cybersecurity focuses on protection, detection, and response. It assumes that with the right controls, breaches can be prevented. Resilience starts from the opposite assumption: breaches are inevitable, and the organization must be built to absorb them without losing its ability to operate or make decisions.
The shift matters because breaches are now a certainty, not a possibility. Resilience builds what practitioners call “shock tolerance,” the capacity to keep functioning when systems are degraded, data is untrusted, and leadership is operating under pressure. That is a fundamentally different engineering problem than building a firewall.
Resilience acts as an integrating umbrella connecting risk management, business continuity, information security, and crisis response as one connected discipline. Without that integration, each function plans in isolation and fails together during a real incident.
The table below clarifies how each discipline differs in scope and objective.
| Discipline | Primary objective | Scope | Focus |
|---|---|---|---|
| Traditional cybersecurity | Prevent and detect threats | IT systems and data | Technical controls |
| Business continuity planning | Keep operations running | Business processes | Operational continuity |
| Disaster recovery | Restore IT systems after failure | IT infrastructure | Speed of restoration |
| Enterprise security resilience | Absorb disruption and adapt | Entire organization | Decision-making under pressure |
The table reveals a critical gap. Disaster recovery measures how fast IT restores systems. Resilience measures whether the organization can still make sound decisions while IT is still down. Those are not the same test.
What are the core components of a security resilience framework?
Effective security resilience programs are built on a combination of technical architecture, governance structures, and continuous assessment. No single tool or policy delivers resilience on its own.
NIST 2026 frameworks require Zero Trust Architecture with continuous identity verification and microsegmentation to contain breaches and limit lateral movement. Zero Trust replaces the old assumption that anything inside the network perimeter is safe. Every access request is verified, every segment is isolated, and a compromised credential cannot roam freely across the environment.
AI plays a central role in modern resilience programs. AI enables continuous probing of access and exposure, shifting security teams from reactive defenders to proactive testers. That shift is not cosmetic. It means vulnerabilities get found by your team before an attacker finds them.
Annual business impact assessments are a non-negotiable foundation. Experts recommend AI automation and yearly impact assessments to address modern threats effectively. These assessments identify which assets are truly critical, so recovery resources go to the right places first.
The essential components of a resilience program include:
- Zero Trust Architecture with microsegmentation and continuous identity verification
- AI-driven threat detection for proactive vulnerability identification and faster response
- Annual business impact assessments to rank and prioritize critical assets
- Isolated backup vaults kept separate from production networks to survive ransomware
- Integrated governance connecting security, continuity, and crisis management teams
- Continuous scanning for configuration drift, exposed assets, and access anomalies
- Tabletop exercises that simulate extreme failure scenarios, not just IT outages
Pro Tip: Do not treat your backup strategy as complete until you verify that backup systems are fully isolated from production networks. Backups on the same network get compromised alongside operational data during ransomware attacks, which eliminates your recovery option at the worst possible moment.
How can enterprises improve security resilience in 2026?
Building resilience maturity is a phased process. Organizations that try to implement everything at once typically end up with disconnected controls that fail under real stress.
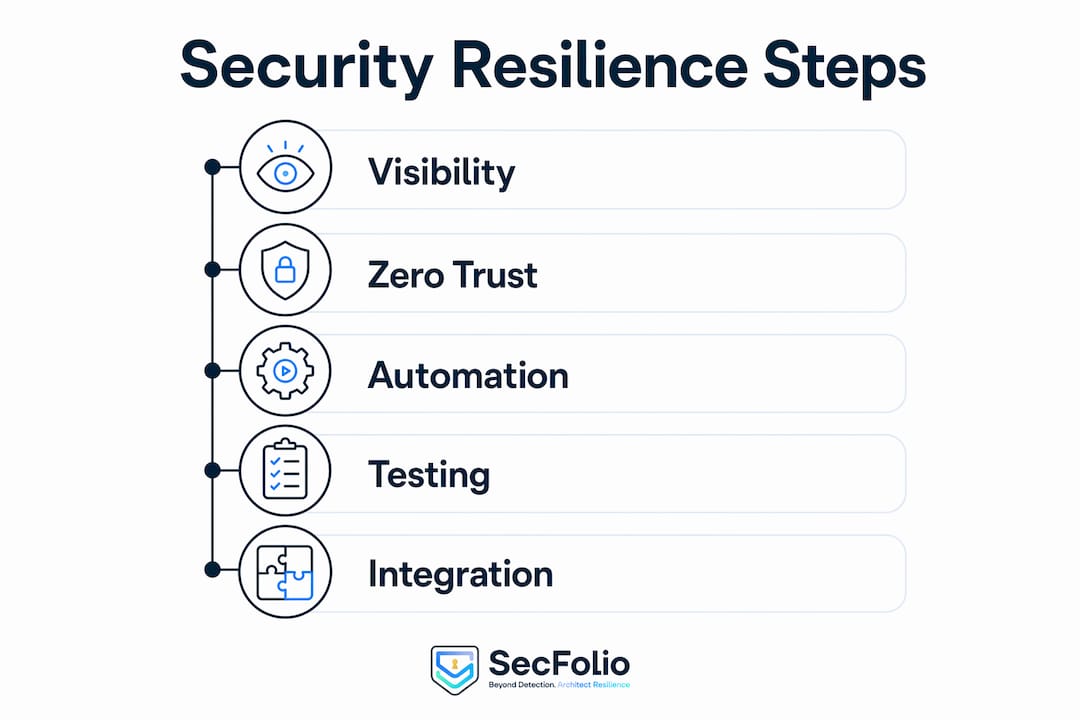
Phase 1: Establish visibility. You cannot protect what you cannot see. Map every exposed asset using an attacker’s perspective, not just your internal asset inventory. Effective resilience includes an attacker’s-eye view that verifies all exposed assets and confirms backups are isolated in secure vaults. Secfolio’s attack surface management capabilities support this kind of external visibility directly.
Phase 2: Implement Zero Trust and microsegmentation. Segment your network so that a compromised identity or endpoint cannot move laterally to reach critical systems. Secfolio’s Identity Microsegmentation approach is built specifically for this phase, containing breaches before they spread.
Phase 3: Automate detection and response. Manual monitoring cannot keep pace with modern attack speeds. Deploy AI-driven detection that continuously tests assumptions and flags anomalies in real time. Secfolio’s Defensive Automation powered by AI addresses this directly by eliminating attack pathways as they form.
Phase 4: Test organizational decision-making, not just IT recovery. Tabletop exercises that simulate worst-case scenarios measure organizational preparedness under pressure. The test is not whether IT can restore a server. The test is whether your leadership team can make sound decisions when data is untrusted and systems are partially down. Testing recovery only after IT restores is insufficient to prove real resilience.
Phase 5: Integrate and iterate. Connect security, continuity, and crisis management into a single program. Resilience programs fail when changes in one area do not propagate through all plans, causing documentation to lose trust and become irrelevant during crises. Review and update all plans together after every significant incident or exercise.
Pro Tip: Avoid the common pitfall of treating resilience as a compliance checkbox. A cyber shock tolerance score assesses your organization’s real ability to absorb and recover from disruption under stress, not just whether you passed an audit. Build toward that standard, not the minimum required for certification.
What role do leadership and culture play in sustaining resilience?
Technical controls alone do not produce resilience. The organizations that recover fastest from major incidents share one trait: their leadership treats cyber risk as a core business capability, not an IT problem.
CISOs now play an expanding role integrating cybersecurity into business strategy and must turn cyber risk into a trust and performance advantage. That requires a seat at the executive table, not just a report delivered to the board once a quarter. When the CISO is part of strategic decisions, resilience gets built into products, processes, and partnerships from the start.
Governance failures are as dangerous as technical gaps. Resilience requires continuous scanning, testing, and a culture that treats complacency as a serious risk. A security program that passed its last audit but has not been stress-tested in 18 months is a liability, not an asset.
Leadership best practices for sustaining resilience include:
- Assign clear ownership for resilience outcomes across security, operations, and business units
- Conduct post-incident reviews that focus on decision quality, not just technical root cause
- Communicate resilience metrics to the board in business terms, not technical jargon
- Reward teams that surface vulnerabilities before attackers do, rather than penalizing failure
- Require cross-functional participation in tabletop exercises, including legal, communications, and finance
External pressure from regulators, customers, and media coverage of breaches also shapes resilience priorities. Organizations that treat these pressures as drivers of genuine improvement, rather than reputation management exercises, build more durable programs over time.
Key Takeaways
Enterprise security resilience requires integrating Zero Trust Architecture, AI-driven detection, isolated backups, and cross-functional leadership to maintain operations and sound decision-making when systems are under attack.
| Point | Details |
|---|---|
| Resilience goes beyond cybersecurity | The goal is maintaining operations and decisions under pressure, not just preventing breaches. |
| Zero Trust is the technical foundation | Microsegmentation and continuous identity verification contain breaches before they spread. |
| Isolate your backups | Backups on the same network as production systems get compromised together during ransomware attacks. |
| Test decision-making, not just IT recovery | Tabletop exercises must simulate extreme scenarios where data is untrusted and leadership must act. |
| Leadership drives sustained resilience | Governance failures are as dangerous as technical gaps; CISOs must have a seat at the business table. |
Why I think most enterprises are testing resilience wrong
Most resilience programs I have observed share the same blind spot. They measure recovery time after IT restores systems. That is the wrong test. Real resilience is about what happens in the hours before IT restores anything, when leadership is making calls with incomplete information, untrusted data, and public pressure building.
The organizations that handle major incidents well are not the ones with the fastest restore times. They are the ones that practiced making decisions in the dark. That means running tabletop exercises where the scenario assumes your backups are compromised, your monitoring is blind, and your communications team is fielding media calls simultaneously. Most security teams never run that exercise.
AI adds a layer of complexity here that I find underappreciated. AI-driven detection is genuinely powerful for proactive threat identification. But it also creates a new dependency. If your team has never operated without AI-assisted alerting, they will struggle when that system is the thing that gets taken down first. Build the human judgment muscle alongside the automation, not instead of it.
The other pattern I keep seeing is siloed planning. Security writes one plan, continuity writes another, and crisis management writes a third. They have never been tested together. When a real incident hits all three simultaneously, the seams show immediately. Integration is not a nice-to-have. It is the difference between a coordinated response and three teams calling each other for instructions while the clock runs.
— James
Secfolio’s approach to building enterprise resilience
Lateral movement is one of the most damaging phases of any breach. Once an attacker gets inside, the ability to move freely across your network determines how much damage they can do before detection. Containing that movement is where resilience programs either hold or collapse.
Secfolio addresses this directly through Identity Microsegmentation and lateral movement prevention, which limits how far a compromised identity or endpoint can reach inside your environment. Combined with Defensive Automation powered by AI, Secfolio continuously identifies and eliminates attack pathways rather than waiting for alerts after the fact. For security managers building toward a Zero Trust model, Secfolio’s prevention-first approach connects directly to the resilience frameworks covered in this guide.
FAQ
What is enterprise security resilience in simple terms?
Enterprise security resilience is an organization’s ability to keep operating and making sound decisions during and after a cyberattack. It goes beyond preventing breaches to absorbing disruption and recovering without losing critical functions.
How does resilience differ from business continuity planning?
Business continuity planning focuses on keeping operations running after a disruption. Resilience is broader, integrating security, continuity, and crisis management into one program that also addresses decision-making under uncertainty.
What frameworks support enterprise security resilience?
NIST frameworks are the primary standard, requiring Zero Trust Architecture, microsegmentation, and continuous identity verification. Annual business impact assessments and AI-driven detection are also core components of current resilience programs.
Why do backup systems fail during ransomware attacks?
Backups stored on the same network as production systems get encrypted or corrupted alongside operational data during ransomware attacks. Effective resilience requires isolating backups in secure vaults completely separate from the production environment.
How should enterprises test their security resilience?
Enterprises should run tabletop exercises that simulate extreme failure scenarios, including situations where data is untrusted and IT systems are not yet restored. Testing only after IT recovery is insufficient to measure real organizational resilience.


