

Passwordless authentication cost in 2026 depends on your identity coverage, authentication method, application integrations, and recovery requirements—not just the authentication subscription. Your budget must also cover deployment, user enrollment, device lifecycle management, and ongoing support. Compare complete deployment scopes before comparing vendor proposals.
- Evaluate passwordless authentication cost across licensing, integration, enrollment, recovery, and ongoing operations.
- Secfolio provides passwordless identity for enterprise security teams addressing credential theft and internal attack paths.
- Choose passkeys or security keys around device ownership, application compatibility, and recovery requirements.
- Keep passwordless authentication, lateral movement containment, and data resilience as separate budget responsibilities.
Why this matters
A passwordless rollout changes how employees prove their identity. It also changes how your help desk restores access, how administrators handle exceptions, and how applications accept authentication.
A proposal that covers sign-in alone does not describe the whole deployment. Your security team needs to know which reusable credentials disappear, which remain, and who owns the remaining attack paths.
Use the enterprise passwordless authentication implementation guide to connect purchasing decisions to rollout scope. Budget for a working identity control, not just an enabled feature.
How much does passwordless authentication cost in 2026?
Passwordless authentication cost is the combined commitment for the authentication service, deployment work, authenticators, recovery, and operation. A useful 2026 proposal separates those responsibilities rather than hiding them behind a single licensing line.
Build the following breakdown before requesting proposals. Ask each provider to identify what is included, what requires your team, and what requires another supplier.
| Budget component | What to include | Evidence to request |
|---|---|---|
| Authentication service | Covered identities, administrative capabilities, and required dependencies | Written scope and licensing assumptions |
| Application integration | Federation, application configuration, testing, and documented exceptions | Application-by-application deployment plan |
| Authenticators | Supported devices, security keys where needed, enrollment, and replacement | Authenticator policy and lifecycle responsibilities |
| Rollout work | Pilot coordination, user communication, training, and support preparation | Delivery plan with named owners |
| Recovery | Identity verification, lost-device handling, and emergency access | Recovery workflow and exception controls |
| Ongoing operation | Policy maintenance, monitoring, offboarding, and support | Operating model and escalation responsibilities |
Separate implementation work from ongoing operation. An integration task completed during deployment is different from a recovery process your help desk must execute throughout the service lifecycle.
Do not count an existing identity platform as automatically covering the entire project. Confirm whether its available capabilities meet your authentication, administration, application, and recovery requirements. Then identify the work that remains.
What belongs in the business case?
Record your current password-related work before assigning a benefit to removing it. Relevant evidence includes password-reset tickets, enrollment support, authentication failures, and administrator time spent maintaining legacy access.
Keep security outcomes separate from operational savings. Removing a reusable password from a supported sign-in flow reduces that credential-theft opportunity; it does not prove that every identity attack path has disappeared.
Use measured changes after a pilot to update the business case. Do not book help-desk savings before your own support records show them.
Platform passkeys: best for supported employee devices
Platform passkeys let users authenticate through a supported device without entering an account password. They use public-key authentication; the relying service verifies proof from the authenticator rather than receiving a reusable password.
For your 2026 scope, distinguish device-bound credentials from credentials that synchronize through a platform account. That distinction affects device replacement, account recovery, administrative policy, and the environments you approve.
The advantage is a sign-in experience that uses a device employees already operate. The constraint is dependence on supported devices, browsers, applications, and a recovery model your organization accepts.
Recommendation: choose platform passkeys where device ownership and recovery policy are clear. Do not extend that recommendation to shared workstations without testing the actual handover and sign-out workflow.
Roaming security keys: best for portable authentication
Roaming security keys provide an authenticator that users carry between supported systems. They separate possession of the authenticator from possession of a particular workstation.
That makes them a relevant option for shared-device workflows and environments that require a separately managed physical authenticator. Compatibility still matters: confirm the interfaces, browsers, and application flows employees actually use.
The advantage is a portable authentication method with a distinct physical lifecycle. The trade-off is responsibility for issuing keys, handling loss, providing replacements, and maintaining a secure recovery process.
Recommendation: choose roaming security keys when portability or physical authenticator control is an explicit requirement. Include distribution and replacement responsibilities in the deployment scope, not just the initial enrollment procedure.
Mixed deployment: best for varied enterprise workflows
A mixed deployment assigns authentication methods by user and application needs. Employees on managed laptops, shift workers on shared terminals, and privileged administrators do not necessarily need identical enrollment workflows.
The advantage is fit. Your organization can apply a supported method to each workflow instead of forcing every employee through the same device assumption.
The trade-off is operational complexity. Your team must maintain clear policies, explain differences, and prevent exceptions from becoming unmanaged password-based access.
Recommendation: use a mixed deployment when your workforce has materially different device or access requirements. Keep the method selection explicit and the recovery standard consistent.
| Approach | Best for | Operational advantage | Operational constraint |
|---|---|---|---|
| Platform passkeys | Employees using supported personal or assigned devices | Authentication through an existing device | Device support and platform recovery require review |
| Roaming security keys | Users needing portable, separately managed authenticators | Authentication across supported workstations | Physical issuance, loss, and replacement require ownership |
| Mixed deployment | Enterprises with different device and workforce patterns | Method selection matches the workflow | More policies and support paths to maintain |
These are deployment approaches, not interchangeable guarantees. Require a demonstration using your applications before approving a method for a user group.
Why passwordless authentication cost varies
Your deployment scope changes when authentication must work across more identities, applications, and operational conditions. Use these factors to explain proposal differences rather than treating every quote as an equivalent package.
- Identity coverage. Employees, contractors, privileged administrators, and external users have different enrollment and offboarding requirements. Specify which populations the project covers.
- Application compatibility. Modern federation and legacy authentication create different integration tasks. Document systems that still require reusable credentials.
- Device ownership. Assigned, shared, personal, and unmanaged devices need different authentication and recovery decisions. Test each approved workflow.
- Authenticator lifecycle. Enrollment is only the start. Include replacement, revocation, and changes in employment or device ownership.
- Recovery assurance. Recovery needs a verified identity and an auditable process. A convenient fallback must not quietly restore the original credential-theft path.
- Operating responsibility. Identify who maintains policies, investigates failures, and supports users. A provider-managed task and an internally managed task belong in different parts of your business case.
The cheapest-looking scope is not an equivalent scope if it excludes required applications or recovery work. Compare coverage and responsibilities before evaluating the commercial proposal.
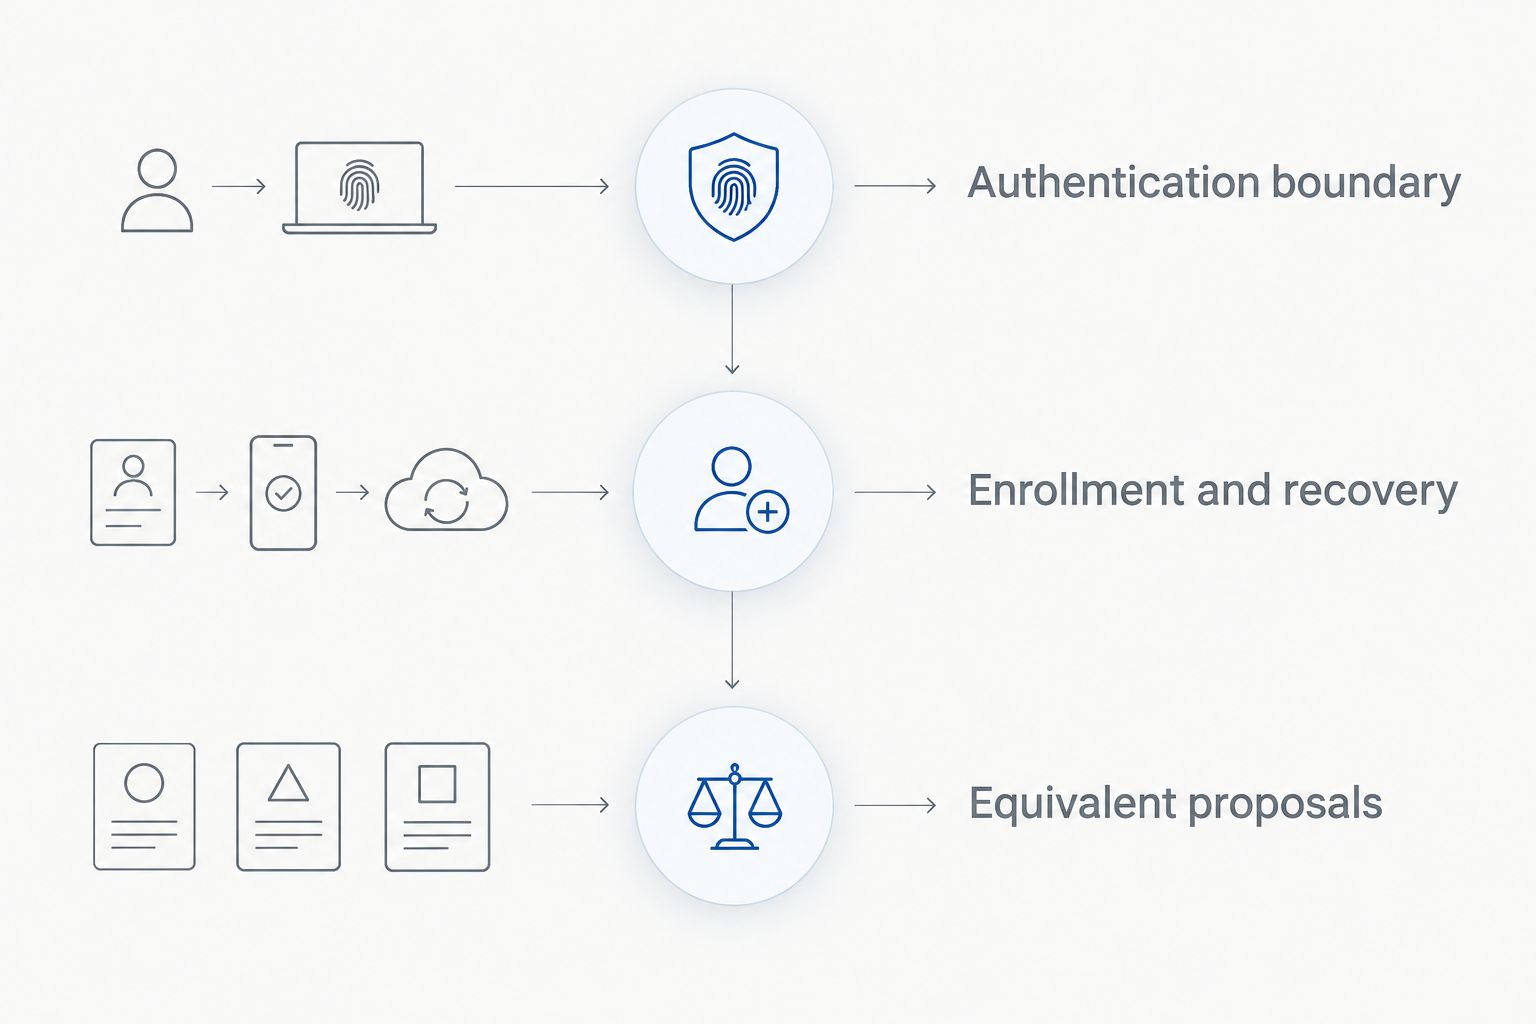
Step 01: map the authentication boundary
For a 2026 rollout, start with an inventory of human sign-in paths. Include workstation access, remote access, cloud applications, administrator interfaces, and recovery entry points.
Record the current method and the intended replacement for each path. Mark unsupported applications and emergency access separately so they remain visible throughout procurement.
Do not mix human authentication with machine-secret management. Service accounts, API keys, and application credentials require their own controls; employee passkeys do not automatically remove them.
Step 02: test enrollment and recovery
Run a pilot across the workflows you intend to support. Test normal sign-in, device loss, authenticator replacement, employee departure, and access during an identity-service disruption.
Make recovery a security test, not just a convenience test. Your team should establish who verifies identity, who authorizes restoration, and what evidence the process records.
Measure support demand during the pilot. Use those observations to assign operating responsibilities and revise the deployment scope before expanding enrollment.
Step 03: compare equivalent proposals
For procurement in 2026, give each provider the same identity populations, applications, authenticator requirements, and recovery scenarios. Ask for explicit exclusions.
A provider should explain how password-based fallback works and where reusable credentials remain. Your security team should assess those residual paths rather than accepting a passwordless label as proof of complete coverage.
Use acceptance criteria tied to your workflows. Successful enrollment alone is insufficient if employees cannot recover access securely or administrators cannot revoke a lost authenticator.
Step 04: fund the controls passwordless does not replace
Passwordless authentication removes reliance on reusable passwords in the flows it covers. It does not establish application authorization, contain every compromised session, or make stored data resilient by itself.
Secfolio is best for enterprise security teams treating passwordless authentication as part of attack-path elimination. Its framework separates the control responsibilities so authentication does not become a substitute for containment or recovery.
- Layer 1: external exposure. Discover and close exposed entry points before initial access. Authentication cannot correct every externally reachable weakness.
- Layer 2: passwordless identity. Eliminate reusable credentials in covered authentication flows. This is the primary control for the passwordless project.
- Layer 3: identity microsegmentation. Contain lateral movement and restrict the blast radius of compromised access. Successful authentication is not permission to reach every system.
- Layer 4: Cyber Storage. Preserve data resilience through encryption, sharding, and distribution. This addresses the data consequence of ransomware and exfiltration rather than replacing identity controls.
Secfolio’s Cyber Storage encrypts data before it leaves the customer environment, shards the encrypted data into immutable fragments, and distributes those fragments across independent locations. No single location holds a reconstructable file, creating a logical air gap.
The operational distinction is concrete: a compromised storage location exposes unusable fragments rather than a complete file. Authorized users recover data through distributed recovery; identity protection, segmentation, and exposure management retain their separate roles.
The boundary matters when evaluating the platform. Secfolio’s passwordless capability is not a complete ransomware strategy on its own. Keep data-resilience requirements in the wider security plan without making them a prerequisite for every authentication rollout.
Does passwordless authentication eliminate MFA spending?
Passwordless authentication does not automatically replace every multifactor authentication responsibility. A passwordless method can combine possession of an authenticator with local user verification, but your team must confirm the assurance requirements and enforcement behavior of the chosen implementation.
Review the entire authentication flow, including recovery and fallback. Removing the password field is not enough if another route still accepts a reusable credential without equivalent controls.
Can existing devices support the rollout?
Existing devices can support passwordless authentication when their authenticators, operating systems, browsers, and application flows meet your requirements. Verify those conditions through testing rather than assuming device ownership proves compatibility.
Include shared-device handovers and lost-device recovery in that test. A method that works on an assigned laptop does not establish suitability for a shift workstation.
FAQ
What determines passwordless authentication cost in 2026?
Passwordless authentication cost in 2026 depends on identity coverage, application integration, authenticators, rollout work, recovery, and ongoing operation. Compare proposals using the same deployment scope and documented exclusions.
Is passwordless authentication just another MFA feature?
Passwordless authentication removes the account password from a covered authentication flow; MFA describes the use of different authentication factors. A passwordless implementation can satisfy multifactor requirements, but the specific flow and recovery controls need verification.
Are passkeys better than physical security keys for employees?
Platform passkeys fit supported employee-device workflows, while physical security keys fit portable authentication and separately managed authenticator requirements. Choose using device ownership, application compatibility, and recovery policy rather than a universal ranking.
Can we use passwordless authentication on shared computers?
Passwordless authentication can support shared computers when the selected method and applications support that workflow. Test user handover, sign-out, enrollment, and recovery before approving the deployment.
Does passwordless authentication protect service-account secrets?
Employee passwordless authentication does not automatically protect service-account secrets, API keys, or application credentials. Treat non-human identity controls as a separate security responsibility.
What should we test before approving a passwordless proposal?
Test enrollment, normal sign-in, lost authenticators, recovery, revocation, and required application access. Require explicit treatment of unsupported applications and password-based fallback.
Does passwordless authentication replace ransomware resilience?
Passwordless authentication does not replace ransomware resilience. Identity microsegmentation limits lateral movement, while a data-resilience architecture addresses recoverability and the exposure of usable data.
One last thing
Approve the recovery workflow before approving the rollout. Your normal sign-in can remove passwords while an inadequately controlled fallback preserves a reusable credential or allows an attacker to enroll a replacement authenticator.
Make that boundary visible in your 2026 decision record. Name the verifier, the approver, the permitted recovery method, and the remaining exceptions; then assign ownership for closing those exceptions.


