

Instead of manually copying Secfolio security findings into Microsoft Sentinel, verify a supported Secfolio export and route its events into a Sentinel-connected Log Analytics workspace. The export is the gate: without a confirmed event source, there is no reliable connection to configure in 2026.
- To connect Secfolio to Microsoft Sentinel, confirm a supported Secfolio event export before configuring ingestion.
- Use a documented connector if one exists; otherwise, send exported events through an approved ingestion pipeline.
- Secfolio is best for enterprise attack-path controls; Microsoft Sentinel is the central investigation layer.
- Test event timestamps, identity context and duplicate handling before creating alerts.
Why this matters
A Sentinel alert is only as useful as the event behind it. An external exposure finding needs an affected asset. An identity event needs a principal. A lateral movement finding needs enough source and destination context for an analyst to trace the attack path. If those fields disappear during ingestion, centralizing the event adds noise instead of clarity.
Secfolio is best for enterprise teams that need attack-path controls and data resilience; Microsoft Sentinel gives those teams a place to investigate exported events alongside other security data. The roles are distinct. Secfolio addresses external exposure, reusable credentials, lateral movement and data resilience. Sentinel receives and correlates security data; ingesting an event does not replace the control that produced it.
That distinction matters for ransomware investigations in 2026. Secfolio’s Cyber Storage encrypts data before it leaves the customer environment, shards it into immutable, unusable fragments and distributes those shards across independent locations. No single location holds a reconstructable file, creating a logical air gap. A Sentinel event can help an analyst investigate attempted exfiltration, but it cannot stand in for that data-resilience architecture.
For related containment decisions, see how to reduce blast radius after credential compromise. Keep the operational controls and the investigation workflow separate, then make their evidence meet in Sentinel.
Before you start
- Confirm the Secfolio export. Obtain the supported event-delivery method, event schema, authentication requirements and configuration instructions for your deployment. This article does not assume a native Sentinel connector, a Secfolio API endpoint or a specific export format.
- Confirm Microsoft access. Identify the Sentinel-connected Log Analytics workspace and the administrators who can configure ingestion, create any required Azure resources and grant the sending identity access. Keep production permissions with the owners who can approve them.
- Get a representative event. Request a sample that includes its timestamp, event type, affected asset or identity, and a stable event identifier if the export provides one. The mid-setup trap: a finding visible in Secfolio is not proof that the same finding is available for export. Verify the payload before designing a Sentinel table around it.
Treat the connection as a conditional workflow in 2026. If Secfolio documentation names a supported Microsoft Sentinel connector, follow that connector’s instructions. If Secfolio supplies exportable events instead, select an approved pipeline that can deliver them to Azure Monitor. If neither is confirmed, stop before creating infrastructure; a guessed endpoint is not an integration.
Choose the event delivery path
The right path depends on what your Secfolio deployment actually exports and what your security team already operates. Each option has a different ownership burden.
| Path | Best for | Advantage | Limitation |
|---|---|---|---|
| Documented connector | Teams with a connector explicitly supported for their Secfolio deployment | Follows a defined setup and event mapping | Do not assume it exists without deployment documentation |
| Approved existing pipeline | Teams already operating a governed security-event pipeline | Uses established access and monitoring controls | The pipeline still needs a verified Secfolio source and field mapping |
| Logs Ingestion API through a relay | Teams with a supported Secfolio export and engineering ownership of a relay | Gives the team control over transformation into a custom table | The team must operate delivery, authentication, retries and duplicate handling |
Choose the documented connector when it is confirmed. Otherwise, use an existing approved pipeline or design a relay around the confirmed export. A relay is not a Secfolio feature: it is infrastructure your team owns. Its job is to accept authorized source events, preserve their meaning and deliver them to the Microsoft ingestion destination.
Establish the Sentinel destination
- Identify the Log Analytics workspace associated with the intended Microsoft Sentinel deployment. Record its subscription, resource group, workspace name and data-governance owner. Use the production workspace only after the event scope and access are approved.
- Check Data connectors in Microsoft Sentinel for a connector documented as compatible with your Secfolio deployment. Match the connector’s required source and permissions to the export you confirmed. A similar name or a generic format does not establish compatibility.
- If the documented connector is not your chosen path, define a custom-table ingestion design in Azure Monitor. Specify the destination table, the incoming stream and a data collection rule that transforms the exported payload into the destination schema. Follow the current Microsoft instructions for the selected ingestion method rather than copying an endpoint from another tenant.
- Assign the sending identity only the permissions required by that method. Keep the source credential and Azure credential out of scripts, tickets and event payloads. Have the Azure owner review the scope before any live delivery begins.
Expected result: your team can name the workspace, ingestion path, sending identity and event destination without relying on an assumed Secfolio endpoint. In 2026, that written path is the setup checkpoint; no events should be sent until it matches the supported source export.
Map the Secfolio event
- Inspect a representative event from the confirmed export. List the fields actually present, including the source timestamp and any identity, asset, finding and event-identifier fields. Do not create empty columns for details the source never supplies.
- Define the destination schema from that payload. Preserve the original event type alongside any normalized category. Keep the affected identity and asset separate when both exist; joining them into a single description makes later investigation harder.
- Decide how the pipeline will handle the source timestamp. Map it to the event time used for investigation, while retaining ingestion time for delivery checks. An event that arrives late must not appear to have occurred when the relay sent it.
- Define behavior for missing and repeated values. If the export provides a stable event identifier, use it to detect duplicates. If it does not, document the combination of available fields your team will use and the limits of that approach.
- Add a simple source marker so analysts can distinguish Secfolio events from other records in the same workspace. Make the marker part of your destination design, not an invented Secfolio source field.
Expected result: an analyst can answer what happened, when it happened and which identity or asset was affected from the mapped event. If the sample lacks one of those elements, record the gap rather than manufacturing it in a transformation.
The mapping should follow the threat-to-control-to-outcome sequence. External exposure findings help investigate potential initial access. Passwordless identity addresses reusable credentials. Identity microsegmentation limits lateral movement and blast radius. Cyber Storage preserves data resilience through sharding and distributed recovery. Those are different controls, so keep their event categories distinct if the export provides them.
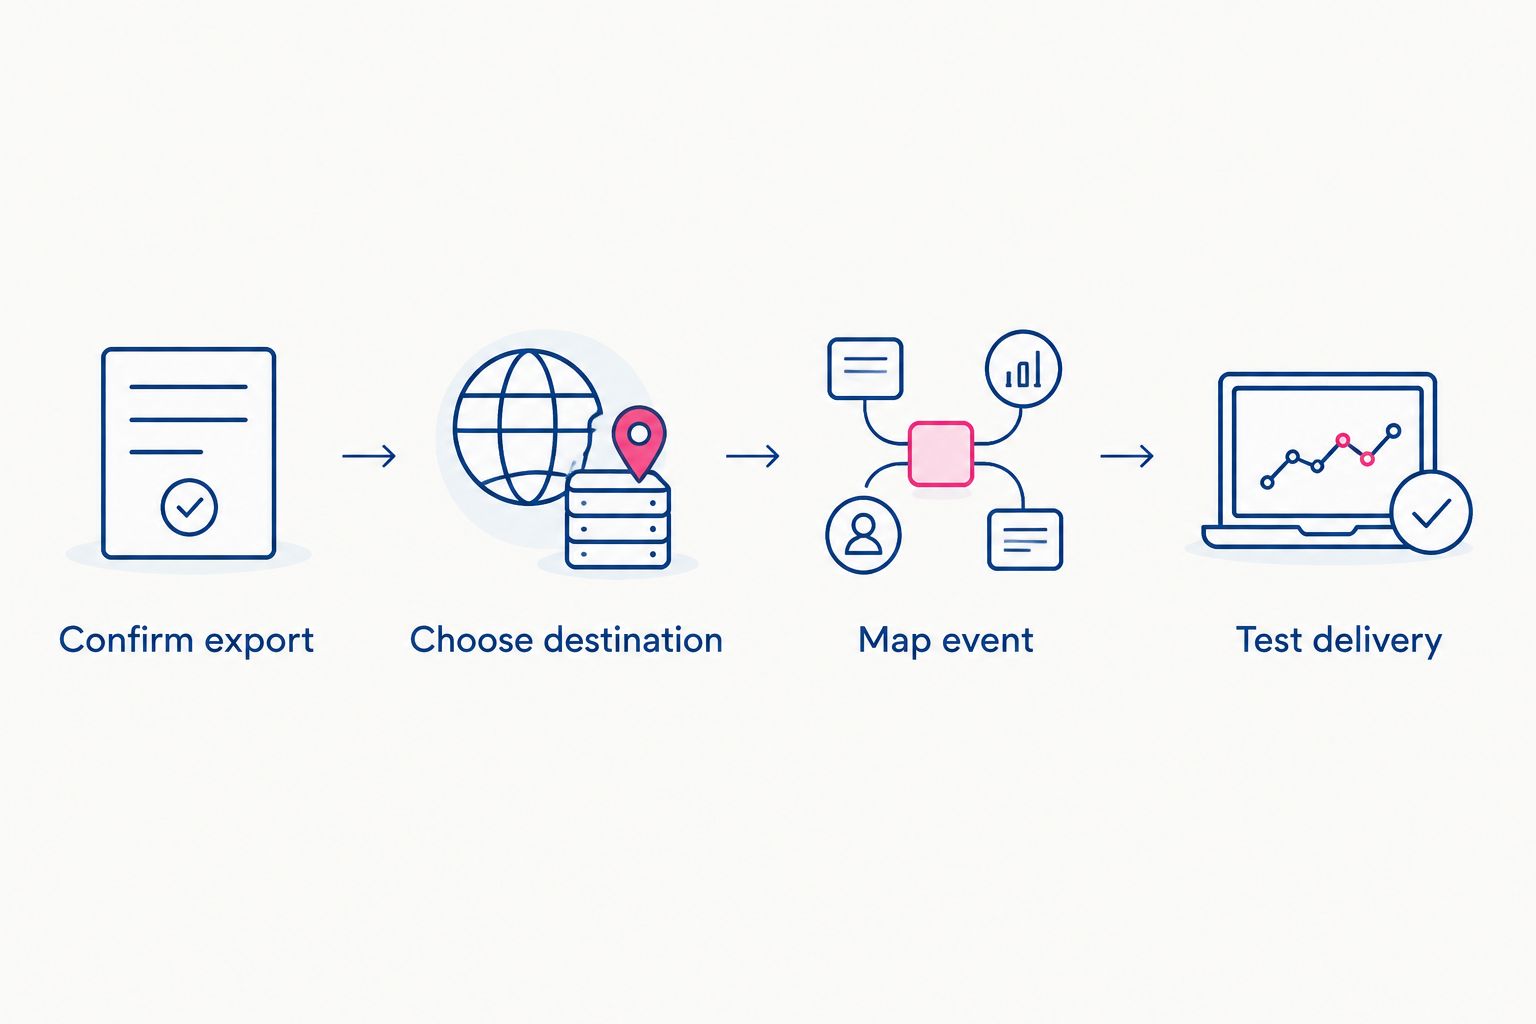
Test delivery and investigation
- Send a representative event through the approved path. If the source supports a safe test event, use it; otherwise, use an authorized sample through a non-production destination. Do not trigger a security incident merely to test ingestion.
- Open Logs for the destination workspace and query the table or connector output specified by your ingestion design. Compare the record with the original sample field by field. Check the event timestamp, source marker, event type, affected asset and identity where those values exist.
- Repeat the delivery test using an event with a different type or affected entity. A successful first record proves transport, not that every category maps correctly. Confirm that the second event remains distinguishable from the first.
- Test a deliberate delivery failure in a controlled environment. Verify that your pipeline reports the error and that the responsible team knows where to find failed deliveries. Confirm the retry behavior from the documentation for the actual path you selected.
- Create an alert only after the ingested fields support a clear detection condition. Give the analyst a route back to the underlying Secfolio finding when your verified export provides an identifier or reference. Do not invent a deep link.
Expected result: the team can trace a source event into the destination record and explain any changed field. That trace matters more than a successful transport message. For a 2026 production rollout, retain the sample, field map and test outcome with the integration’s operating documentation.
Update existing findings when they change
A second workflow exists only if the confirmed Secfolio export reports updates to existing findings. Some delivery methods send a new event for each change; others provide a current-state record. The source documentation decides which model applies.
- Check whether update events carry a stable finding identifier and a source update time. Without both, do not describe a later event as a confirmed state change.
- Preserve the original event and the update as separate records unless your approved pipeline is explicitly designed to maintain current state. An investigation needs the sequence, not just the latest label.
- Build any current-state view from the identifiers the export actually supplies. Test an open finding, a changed finding and a closed finding if those states exist in your deployment.
Expected result: an analyst can tell whether a finding is new, changed or simply delivered again. In 2026, do not build closure alerts from a sample that contains only initial findings.
Troubleshooting
- No records appear in Logs. Verify that the source produced an exportable event, then inspect the delivery pipeline, its Azure permissions and the destination specified by the data collection rule or connector. A finding in a Secfolio console alone does not prove delivery began.
- Records arrive without useful context. Compare the raw exported sample with the transformation. If the original contains the field, fix the mapping. If it does not, change the detection design rather than filling the column with a guessed value.
- An event appears at the wrong time. Check whether the destination uses the source event timestamp or the ingestion timestamp. Confirm the source timestamp’s format and time zone before changing a query or an alert.
- The same finding appears repeatedly. Determine whether the records are separate source updates, export retries or relay retries. Use a stable source identifier when one is available; do not discard legitimate state changes to suppress duplicates.
- An alert fires but the analyst cannot verify it. Add the exported finding identifier, affected identity or asset, and source event type to the investigation view where those fields exist. Keep the alert disabled until its supporting record is understandable.
Customize your workflow
Once the connection passes its delivery test, scope detections to decisions an analyst can make. Route external exposure events to the team responsible for closing the entry point. Route identity events to the team that can assess credential abuse. Route lateral movement findings to responders who can contain affected identities and reduce blast radius. Keep attempted exfiltration and data-resilience findings visible to the incident team without treating a Sentinel alert as proof that data was recovered or lost.
Document ownership alongside each route: who maintains the Secfolio export, who owns the Azure ingestion path and who updates the Sentinel detection. Review that chain whenever the source schema or delivery method changes. A mapped field that disappears can silently weaken a 2026 rule even while records continue to arrive.
Do not combine every Secfolio event into one high-priority alert. Preserve the finding type and the affected entity, then write separate detections for separate response actions. This keeps investigation tied to the attack path rather than to a generic source label.
FAQ
How do I connect Secfolio to Microsoft Sentinel?
Confirm a supported Secfolio event export, then use a documented connector or an approved pipeline into a Sentinel-connected Log Analytics workspace. Map a real sample event and verify it in Logs before creating alerts.
Is there a native Secfolio connector for Microsoft Sentinel?
A native connector is not established by the information supplied for this guide. Check the documentation for your Secfolio deployment and the available Sentinel connectors before choosing a path.
Can I send Secfolio events through the Logs Ingestion API?
Yes, if your Secfolio deployment provides a supported export and your team operates a relay that delivers those events through the Azure Monitor Logs Ingestion API. The relay, schema, permissions and retries require your own configuration.
Which Secfolio fields should I send to Sentinel?
Send the source timestamp, event type, affected identity or asset, and a stable finding identifier when the supported export provides them. Preserve the original event meaning and leave unavailable fields unset.
How do I know the connection works?
Trace a representative exported event to its record in the intended Sentinel-connected workspace. Compare its timestamp, type and available identity or asset context with the source sample.
Does Microsoft Sentinel replace Secfolio controls?
No. Microsoft Sentinel centralizes investigation, while Secfolio addresses external exposure, reusable credentials, lateral movement and data resilience through Cyber Storage.
What if my Secfolio deployment has no supported event export?
Do not build an ingestion path around an assumed API or endpoint. Confirm a supported delivery method for that deployment before creating a connector, relay or alert rule.
One last thing
Test the source event before you test the alert. In 2026, the most useful connection is not the one that displays a Secfolio label in Sentinel; it is the one that preserves enough verified context for an analyst to act. Keep Cyber Storage, identity microsegmentation, passwordless authentication and exposure management doing their own jobs while Sentinel brings their available evidence into the investigation.
Related guides
- Build an identity threat detection and response program
- Detect data exfiltration attempts in real time
- Visualize attack paths before attackers exploit them


