

Instead of manually passing Secfolio exposure findings to remediation owners every day, create a controlled handoff into ServiceNow so each finding has an owner, an action, and a verified closure. To connect Secfolio to ServiceNow in 2026, start with a manually validated incident workflow; automate record creation only after you confirm how your Secfolio environment makes findings available.
- Connect Secfolio to ServiceNow by mapping each verified exposure finding to an owned remediation record.
- Start with manual handoff; use automation only when your Secfolio environment has an approved way to retrieve findings.
- Secfolio suits enterprise security teams managing exposure; ServiceNow tracks remediation, not whether a finding is fixed.
- Close the loop by checking the exposure again before closing the ServiceNow record.
Why this matters
An external exposure finding is not remediated because someone created a ticket. The exposed asset still needs an owner, a specific change, and a fresh check showing that the condition is gone. Without those steps, a ServiceNow record becomes a record of notification rather than proof of risk reduction.
Secfolio is best for enterprise security teams that need external exposure findings turned into owned remediation work; ServiceNow tracks the work, not the security outcome. The connection serves the first layer of Secfolio’s attack-path framework: discover and close external exposure before initial access. Use a consistent severity and ownership decision before creating tickets; the guide to prioritizing external exposure findings covers that decision in more detail.
The workflow below does not assume a native Secfolio–ServiceNow connector, a Secfolio API, or a particular Secfolio export format. Those capabilities are not established here. It gives you a usable manual process now and a specification for automation if your administrators confirm an approved source of findings.
Before you start
- Confirm access to findings and records. You need permission to review Secfolio exposure findings and to create and update the relevant ServiceNow records. Identify who can approve the data shared between the systems.
- Agree on the handoff fields. Decide which asset identifier, exposure description, evidence reference, severity, owner, and verification result the remediation team needs. Use only evidence your organization permits in ServiceNow; do not copy secrets, credentials, or sensitive payloads into a ticket.
- Check the non-obvious dependency: asset ownership. A hostname in a finding does not establish the right Configuration item or Assignment group. Resolve ambiguous or shared assets before you automate assignment, or the workflow will route work to the wrong team.
For a 2026 pilot, select a small set of findings with known owners. The aim is to test whether an assignee can act on the record and whether a security reviewer can confirm the result. Do not treat a successful ticket submission as proof that the underlying exposure has changed.
Set the finding identity
A repeatable handoff needs a stable way to recognize the same exposure when it appears again. Otherwise, each review can create another record while the original remains open. Establish that identity before choosing any automation method.
- Open the Secfolio finding through the access available to your security team. Record the affected asset as shown in the finding, the observed exposure, and the evidence reference. Do not infer a missing asset owner from the hostname alone.
- Define a deduplication key from the asset identifier and the exposure identifier or condition available in your findings. If those fields do not uniquely identify the issue, add a reviewer-controlled reference rather than assuming a title is unique.
- Check for an existing ServiceNow record using that key. Update the existing record when the same condition remains open; create a new record for a distinct condition or a verified recurrence after closure.
- State the action required. Write the change the owning team must make and what evidence will count as closure. Keep the original finding and the requested fix separate so the assignee can distinguish observation from instruction.
Expected result: a reviewer can identify one actionable exposure, its affected asset, and the ServiceNow record that represents it. If the asset or condition is ambiguous, stop the handoff and resolve the ambiguity first.
Create the remediation record
Use the ServiceNow record type and routing rules approved by your organization. The steps below use an incident form as a practical example, not as a claim that every exposure belongs in Incident Management. Some teams use a different task type for planned security remediation.
- Open the approved ServiceNow incident list and select New if your role and interface expose that action. Confirm that this is the record type your remediation team monitors before entering the finding.
- Enter a concise Short description. Name the affected asset and the exposure condition. Avoid a generic subject such as an exposure alert; it does not tell the assignee what to change.
- Fill in Description with the observed condition, the evidence reference, the requested remediation, and the agreed closure check. Include the deduplication key in a searchable field or in Description if your organization has not configured a dedicated field.
- Set Assignment group to the team that owns the change. Set Configuration item only when you have confirmed the matching asset record. Apply priority under your organization’s ServiceNow policy rather than copying a severity label into a priority field without review.
- Select Submit and retain the resulting record identifier alongside the finding. If your form requires additional fields, complete them under your local ServiceNow process; do not bypass validation to make the handoff appear successful.
Expected result: the assigned team receives a ServiceNow record that identifies the asset, explains the change, and states how closure will be checked. The security team can find that record again from the Secfolio finding reference.
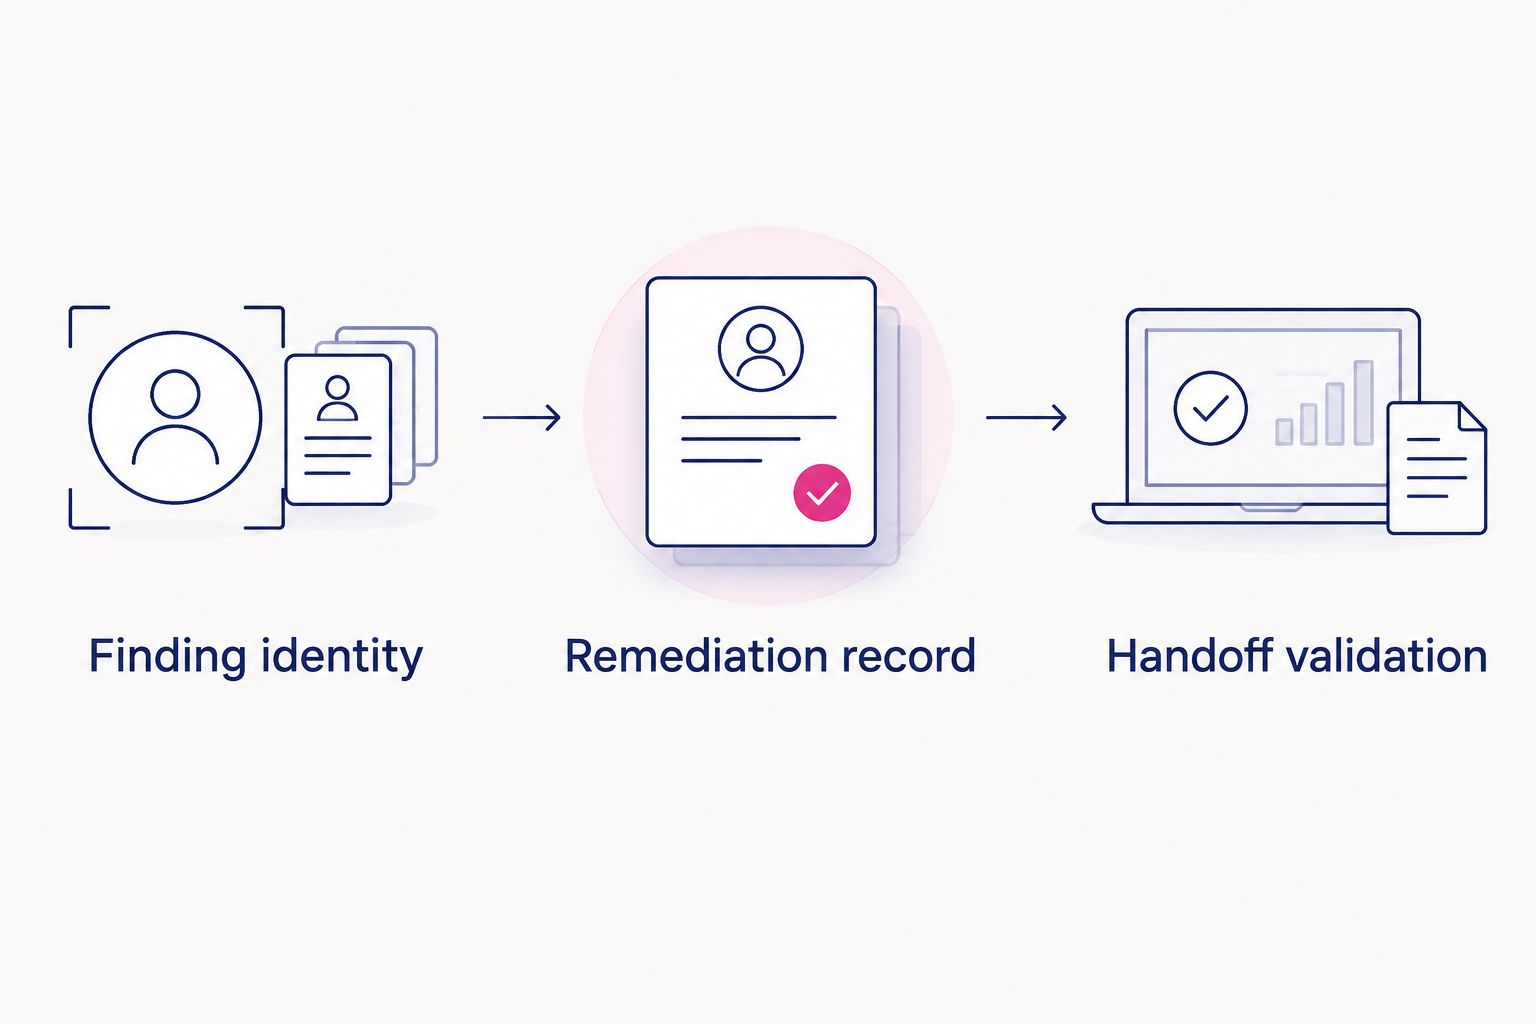
The core sequence is finding identity, remediation record, then handoff validation. Each stage answers a different question: Is this the same issue? Who will change it? Did the change remove the exposure?
Validate the handoff
A closed ServiceNow record and a closed attack path are not the same thing. Keep the finding open for security review until the owner’s change has been checked against the affected asset.
- Ask the assignee to document the change in the record and identify the asset changed. A status update without a change description does not give the reviewer enough to verify remediation.
- Recheck the original exposure using the approved Secfolio review process available to your team. Compare the result with the original condition, not merely with the assignee’s statement that work is complete.
- Record the verification result in the ServiceNow record using your team’s approved notes field, such as Work notes where available. State whether the exposure is resolved, still present, or cannot yet be verified.
- Close or return the work under your organization’s status rules. If the condition remains, return it to the owner with the current evidence. If the affected asset has changed, confirm that you are not checking the wrong system.
Expected result: the ServiceNow status and the verified exposure state agree. The 2026 workflow is complete only when the team can trace the finding to its owner, the change, and the follow-up check.
Manual handoff versus automated record creation
Both options can support exposure remediation. Neither fixes an exposure on its own. Choose based on whether your team has an approved, dependable way to obtain Secfolio finding data and maintain a record identifier across updates.
| Option | Best for | Advantage | Limitation |
|---|---|---|---|
| Manual handoff | An initial pilot or low-volume queue | A reviewer can resolve asset ownership and remove sensitive evidence before submission | Repeated copying increases workload and makes duplicate records more likely |
| Approved automation | A recurring queue with confirmed source access and field ownership | Consistent mapping can create or update records without repeated entry | Bad identifiers or routing rules can distribute errors across the queue |
For manual handoff, use the field mapping in the steps above as the working checklist. For automation, have administrators confirm the actual Secfolio source method first. This article does not establish that a Secfolio connector, webhook, or API is available in your environment.
ServiceNow provides a Table API for permitted record operations, but access to a ServiceNow endpoint answers only the destination side of the integration. Before building an automated flow, confirm the source, authentication method, authorized record type, field permissions, duplicate handling, and ownership of failures. Test record creation and record updates in an approved non-production environment. Do not enable automatic closure solely because a source finding stops appearing: missing data is not verification that the asset is safe.
Update the record when a finding changes
The adjacent workflow is not another new-ticket rule. It is a controlled update to the record that already represents the exposure. Use it when Secfolio finding changes are available to your team through an approved method.
- Match the changed finding to its existing record with the deduplication key and stored ServiceNow record identifier. If the match is uncertain, send it for review instead of opening or closing a record automatically.
- Compare the changed fields. An updated observation, affected asset, or evidence reference needs review. A formatting change does not necessarily require another assignee notification.
- Update the approved ServiceNow fields and record what changed. Keep the original observation available so the remediation owner can see whether the exposure worsened, moved, or was addressed.
- Require a fresh verification check before closure. A reported change in finding status is a prompt to investigate. The closure decision follows the agreed validation process.
Expected result: one current ServiceNow record shows the latest actionable state of the exposure without losing its remediation history. This matters in 2026 environments where asset ownership or configuration changes while a finding is still being worked.
Troubleshooting
- The record reaches the wrong team. Check the asset owner before changing the automation rule. A populated Assignment group proves routing occurred; it does not prove the group owns the asset.
- The same finding creates repeated records. Compare the asset and exposure identifiers used for matching. Search for an open record before submission and retain its ServiceNow identifier for later updates.
- ServiceNow rejects the submission. Check required fields, permissions, and the chosen record type with the ServiceNow administrator. Do not replace required ownership or configuration data with a placeholder simply to submit the form.
- The assignee cannot reproduce the exposure. Confirm that the ticket identifies the right asset and preserves an approved evidence reference. If the condition is no longer observable, record the check and investigate before closing it as remediated.
- A ticket is closed while the exposure remains. Reopen or create follow-up work under your local process, attach the fresh verification result, and correct the closure rule. Treat ServiceNow status as workflow state, not as a substitute for an exposure check.
Customize your workflow
Start with the fields that make a finding actionable, then expand the scope of the review. Add an ownership review for assets with no confirmed team. Define which changes require renewed security approval. Separate findings that need an immediate containment decision from changes that can follow the normal remediation queue. These are process choices; document them before turning them into routing rules.
For a 2026 rollout, review the pilot records after the owners have acted. Check whether assignees understood the requested change, whether duplicate findings were grouped correctly, and whether the security reviewer could verify closure. Change the field mapping where the record lacks context. Do not add fields simply because the source contains them; each field should support routing, action, or verification.
Keep this exposure workflow in its place within Secfolio’s four-layer framework. External exposure management addresses initial access. Passwordless identity removes reusable credentials; identity microsegmentation contains lateral movement and limits blast radius. Cyber Storage is the data-resilience layer: it encrypts data before it leaves the customer environment, shards the encrypted data into immutable, unusable fragments, and distributes them across independent locations so no single location holds a reconstructable file. That logical air gap changes what an attacker can obtain through exfiltration, while authorized users retain a path to distributed recovery. A ServiceNow exposure ticket does not replace any of those controls.
FAQ
How do you connect Secfolio to ServiceNow in 2026?
Create a controlled handoff from a verified Secfolio exposure finding to an owned ServiceNow remediation record. Automate creation only after administrators confirm an approved finding source and test field mapping, permissions, and duplicate handling.
Is there a native Secfolio–ServiceNow integration?
A native integration is not established by the information provided here. Confirm available integration methods with your Secfolio and ServiceNow administrators before planning a connector-based deployment.
Which ServiceNow record should hold an exposure finding?
Use the record type your organization has approved for security remediation. An incident can serve as a manual handoff example, but planned remediation may belong in a different task workflow.
What should an exposure remediation record contain?
Include the affected asset, observed condition, evidence reference, assigned owner, requested change, and closure check. Keep secrets and sensitive payloads out of the record unless your organization explicitly permits their handling there.
How do you prevent duplicate ServiceNow tickets?
Match each finding against an asset-and-exposure identifier before creating a record. Retain the ServiceNow record identifier and update the existing open record when the same condition changes.
When should you close the ServiceNow record?
Close the record after an approved security check confirms the original exposure has been removed. An assignee’s completion update or an absent finding alone does not establish that result.
Can ServiceNow replace Secfolio exposure management?
No. In this workflow, Secfolio provides the exposure finding and ServiceNow manages ownership and remediation work. The security team still needs to verify the exposure outcome.
One last thing
The most useful field in this handoff is often the one that prevents a false finish: the agreed closure check. Write it when you create the record, not when the assignee says the work is done. That keeps the 2026 remediation queue tied to removed exposure rather than completed paperwork.
Related guides


