

An internal data vulnerability assessment is the structured process of identifying, analyzing, and prioritizing security weaknesses within your organization’s own environment. Security teams call this practice vulnerability management when it runs continuously, but the assessment phase is where everything starts. Standards like ISO 27001 and the NIST Cybersecurity Framework both require regular internal assessments as a baseline control. Without them, enterprises operate blind to the threats already inside their perimeter. The internal data vulnerability assessment steps covered here follow a proven methodology: scope, inventory, scan, analyze, prioritize, remediate, and verify.
What prerequisites are needed before starting internal vulnerability assessment steps?
Preparation determines whether your assessment produces real findings or a false sense of security. Before any scan runs, you need a defined scope, a validated asset inventory, and a clear set of success criteria. Skipping this phase is the most common reason assessments miss critical infrastructure.
Defining scope and success criteria
Scope defines what you will assess and what you will not. A tight scope prevents wasted effort on low-risk systems while protecting high-value assets. Success criteria give your team a measurable finish line. Clear done criteria such as 95% asset coverage and defined remediation windows prevent analysis paralysis and stalled remediation cycles.
Building your asset inventory
Your asset inventory is the foundation of any internal vulnerability assessment checklist. Pull data from your configuration management database, network discovery tools, and cloud asset registers. Cross-reference all three sources because each one will have gapped the others fill. Shadow IT and unmanaged IoT devices are the assets most likely to be missing, and they are often the easiest targets.
Selecting scan types and tools
The choice between authenticated and unauthenticated scans changes what you find. Unauthenticated scans show what an attacker sees from the network. Authenticated scans reveal patch status and configuration flaws that are invisible from the outside. That deeper visibility is worth the added setup time.
| Scan type | What it finds | Key limitation |
|---|---|---|
| Unauthenticated | Exposed services, open ports | Misses patch and config detail |
| Authenticated | Patch gaps, misconfigurations | Requires credential management |
| Manual review | Logic flaws, process weaknesses | Time-intensive, needs skilled staff |
| Penetration test | Chained attack paths | Annual cadence, not continuous |
Pro Tip: Restrict scan accounts to read-only permissions. Overprivileged scan credentials create new attack vectors and undermine the security posture you are trying to measure.
Schedule scans during low-traffic windows and notify operations teams in advance. An unannounced scan on a production database can trigger incident response procedures and waste hours of your team’s time.
How to execute the core internal vulnerability assessment steps effectively?
Execution is where most teams either capture real risk or generate noise. A structured methodology covering discovery, scanning, and validation prevents missing critical infrastructure components like shadow IT and unmanaged devices.
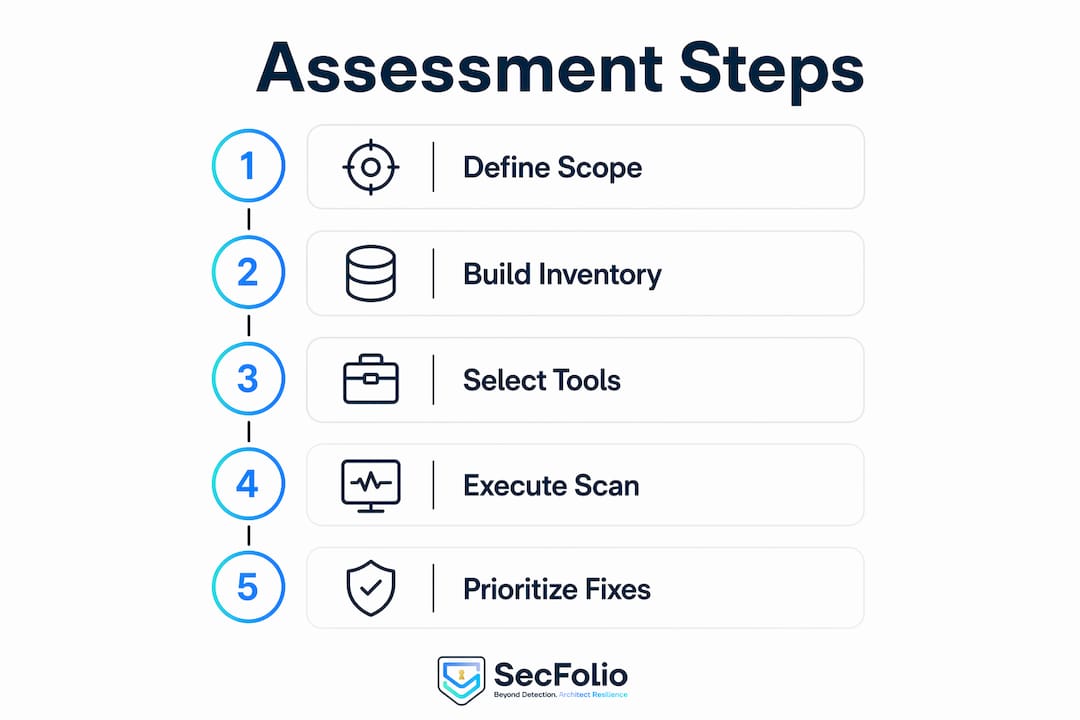
Step-by-step execution process
- Discovery. Run a live host scan across all in-scope IP ranges. Identify open ports and running services. Flag any hosts not in your asset inventory immediately.
- Authenticated scanning. Deploy credentialed scans against all discovered hosts. Collect patch status, software versions, and configuration baselines. Handle credentials through a secrets manager, not a shared spreadsheet.
- Unauthenticated scanning. Run a parallel unauthenticated scan to capture the attacker’s external view of internal segments. Compare results against the authenticated scan to find discrepancies.
- Manual configuration review. Check firewall rules, Active Directory group policies, and service account permissions by hand. Automated tools miss logic flaws and overly permissive access rules that a trained analyst catches in minutes.
- Vulnerability identification and deduplication. Aggregate findings from all scan sources into a single register. Remove duplicates and false positives before scoring begins.
- Risk scoring. Apply CVSS scores as a starting point, then layer in EPSS data and business impact to produce a final risk rating for each finding.
Pro Tip: Run your authenticated and unauthenticated scans within the same 24-hour window. Comparing results from different days introduces configuration drift that skews your findings.
Common mistakes to avoid
- Scanning only internet-facing systems and ignoring internal segments
- Using the same scan profile for workstations and servers
- Accepting scanner output as final without manual validation
- Failing to document scan credentials and their expiration dates
Annual manual penetration testing alongside automated scans catches logic flaws and business process weaknesses that no tool detects on its own. Pen testers think like attackers, which produces findings that automated scans structurally cannot generate.
How to prioritize, remediate, and verify vulnerabilities within internal environments?
Prioritization is where most data security assessment processes break down. Teams fix what is easiest, not what is most dangerous. A risk-based approach changes that.
Less than 1% of CVEs are ever weaponized in the wild. That fact means a raw list of 2,000 scanner findings is not a to-do list. Effective prioritization combines CVSS base scores, EPSS exploit probability scores, active threat intelligence, and the business criticality of the affected asset.
Setting remediation SLAs
Critical vulnerabilities require remediation within 48–72 hours. Medium severity findings should close within 30 days. Low severity items belong in a tracked backlog with a defined review cycle, not a forgotten spreadsheet.
- Assign each finding to a named owner, not a team. Shared ownership means no ownership.
- Track remediation status in a centralized register with weekly status reviews.
- Set an escalation trigger for any critical or high finding unpatched after 90 days. Vulnerabilities unpatched beyond 90 days require escalation to executive management to prevent process failure.
- Run verification scans within 48 hours of a reported fix to confirm the vulnerability is closed, not just patched on paper.
Linking vulnerabilities to business processes converts technical findings into prioritized risk items that leadership can act on. A critical finding on a payment processing server carries different weight than the same finding on a test workstation. That context is what turns a vulnerability report into a resource allocation decision.
Pro Tip: Build a one-page executive summary for each assessment cycle. Show the number of critical findings, the remediation rate, and the trend over time. Leadership approves budgets based on trends, not technical details.
Enterprises should run automated vulnerability scans quarterly on internal systems and monthly on internet-facing systems at minimum. That cadence keeps the finding register current and prevents the backlog from growing faster than the team can close it.
What are common challenges and best practices in internal vulnerability assessments?
Every enterprise assessment program hits the same friction points. Knowing them in advance lets you design around them rather than react to them.
Common challenges
- Incomplete asset discovery. Cloud workloads, contractor devices, and IoT endpoints routinely fall outside standard discovery scans. A missing asset is an unmanaged risk.
- Scope errors. Scanning too broadly wastes time and creates noise. Scanning too narrowly leaves gaps that attackers exploit.
- Overprivileged scan credentials. Scan accounts with administrative rights become high-value targets if compromised. Scoped read-only credentials are the correct practice.
- False positive noise. High false positive rates cause teams to distrust scanner output and skip manual validation. Tune your scan profiles before each cycle.
Best practices that separate effective programs from checkbox exercises
“Continuous vulnerability assessment aligns security operations with business risk management rather than just IT maintenance.” This shift in framing changes how leadership funds and prioritizes the program.
Treating vulnerability assessment as a continuous operational loop with defined done criteria is what separates effective programs from annual checkbox exercises. The loop runs: scope, scan, analyze, remediate, verify, and repeat. Each cycle should produce a measurable improvement in your risk posture.
Blend automated scanning with annual manual penetration testing to capture what tools miss. Communicate findings to operations teams before remediation begins, not after. Ops teams know which systems cannot tolerate downtime during patching, and that knowledge prevents remediation from creating new incidents. Use each assessment report to update your internal security evaluation guidelines and feed lessons learned back into the next cycle’s scope definition.
Linking findings to business processes gives compliance officers the language they need to report risk to boards and auditors. A finding described as “CVE-2024-XXXX on server X” means nothing to a CFO. The same finding described as “an exploitable flaw on the system that processes all customer payments” gets immediate attention and budget.
Key takeaways
A structured, continuous internal data vulnerability assessment process is the most reliable way to reduce enterprise risk before attackers find what your scanners miss.
| Point | Details |
|---|---|
| Scope and inventory first | Define assessment boundaries and validate your asset inventory before any scan runs. |
| Use authenticated scans | Credentialed scans reveal patch gaps and misconfigurations that unauthenticated scans cannot see. |
| Prioritize by business impact | Combine CVSS, EPSS, and asset criticality to fix the vulnerabilities that matter most first. |
| Set and enforce SLAs | Critical findings close in 48–72 hours; escalate anything unpatched beyond 90 days to leadership. |
| Run continuous cycles | Treat assessment as an ongoing loop, not a one-time project, to keep pace with evolving threats. |
What I’ve learned from running internal assessments at scale
The biggest mistake I see enterprises make is treating the assessment as the deliverable. Teams spend weeks scanning, produce a 200-page report, and then watch remediation stall because nobody defined what “done” looks like before the scan started. The report is not the outcome. Closed vulnerabilities are the outcome.
The second pattern I see consistently is over-reliance on CVSS scores. A CVSS 9.8 finding on an air-gapped test system is less urgent than a CVSS 7.0 finding on your domain controller. Scores without business context produce a remediation queue that does not reflect actual organizational risk. I always push teams to map every critical finding to a named business process before assigning a remediation priority.
Credential management during assessments is another area where I see teams cut corners. Scan accounts with domain admin rights are a gift to any attacker who intercepts them. Scoping credentials to read-only is not optional. It is the difference between an assessment tool and a new attack vector.
The teams that run the most effective programs share one trait: they treat the assessment cycle as an operational rhythm, not a compliance event. They scan, fix, verify, and scan again. Each cycle is shorter and more targeted than the last because they learn from what they found before. That compounding effect is what actually moves the risk needle over time.
— James
How Secfolio supports your vulnerability assessment and remediation program
Identifying vulnerabilities is only half the work. Containing the risk they represent requires controls that stay active between assessment cycles. Secfolio’s lateral movement prevention limits how far an attacker can move after exploiting a finding your team has not yet patched. That containment buys your remediation team the time they need without leaving the business exposed. Secfolio’s configuration management capabilities prevent security drift after remediation, so a closed vulnerability stays closed. For enterprises running continuous assessment programs, Secfolio’s prevention approach connects assessment findings directly to enforcement controls across your internal environment.
FAQ
What is an internal data vulnerability assessment?
An internal data vulnerability assessment is a structured process that identifies, scores, and prioritizes security weaknesses within an organization’s own network, systems, and applications. It differs from external assessments by focusing on threats that originate or persist inside the perimeter.
How often should internal vulnerability scans run?
Enterprises should run automated scans on internal systems at least quarterly and on internet-facing systems monthly. Any critical finding unpatched beyond 90 days requires escalation to executive management.
What is the difference between authenticated and unauthenticated scans?
Authenticated scans use valid credentials to access systems and reveal patch status and configuration flaws. Unauthenticated scans show only what an attacker without credentials can see from the network.
How should teams prioritize vulnerability remediation?
Effective prioritization combines CVSS base scores, EPSS exploit probability data, active threat intelligence, and the business criticality of the affected asset. Less than 1% of CVEs are ever weaponized, so raw CVSS scores alone produce a misleading remediation queue.
When should manual penetration testing supplement automated scanning?
Industry practice calls for annual manual penetration testing alongside automated scans. Pen testers uncover logic flaws, chained attack paths, and business process weaknesses that automated tools cannot detect.


