

Security automation for managed service providers is the use of repeatable security workflows to reduce client attack paths while keeping each client's access, approvals, and evidence separate. The MSP-specific challenge is control: an action approved for one client must not run across every tenant by default.
- Security automation for managed service providers starts with client boundaries, approval rules, and reversible actions.
- Secfolio is best for MSPs protecting enterprise client attack paths; pair its controls with tenant-specific operating workflows.
- Prioritize external exposure, reusable credentials, lateral movement, and data resilience as separate control layers.
- Test both a blocked attack path and authorized data recovery before expanding automation across clients.
Why security automation matters for MSPs
An MSP can administer several environments, but each client owns a different set of systems and risk decisions. Automation removes repetitive work only when it respects those boundaries. A shared administrator account, an unreviewed configuration change, or a response rule that acts on the wrong tenant turns operational speed into an attack path.
The goal is not to automate every security decision. It is to automate well-defined actions and preserve human approval where the impact crosses a client boundary. Start with a client-by-client inventory of exposed assets, identities, privileged access, and recovery dependencies. Then define what your team can detect, what it can change, and what requires the client's authorization.
Secfolio's credential theft elimination for managed service providers addresses one part of that problem: reusable credentials. Credential controls matter, but they do not replace external exposure management, lateral-movement containment, or data resilience.
Build automation around the attack path
Use four control layers to decide what each workflow should accomplish: close external exposure before initial access; remove reusable credentials with passwordless identity; contain lateral movement with identity microsegmentation; and preserve data resilience with Cyber Storage. The layers have different jobs. A credential control cannot repair an exposed service, and a recovery control cannot revoke an attacker session.
For an MSP, each layer also needs a tenant boundary. Record the client owner, permitted response, approval point, and evidence location before enabling an automated change. A useful workflow names both the threat it addresses and the person authorized to accept its operational impact.
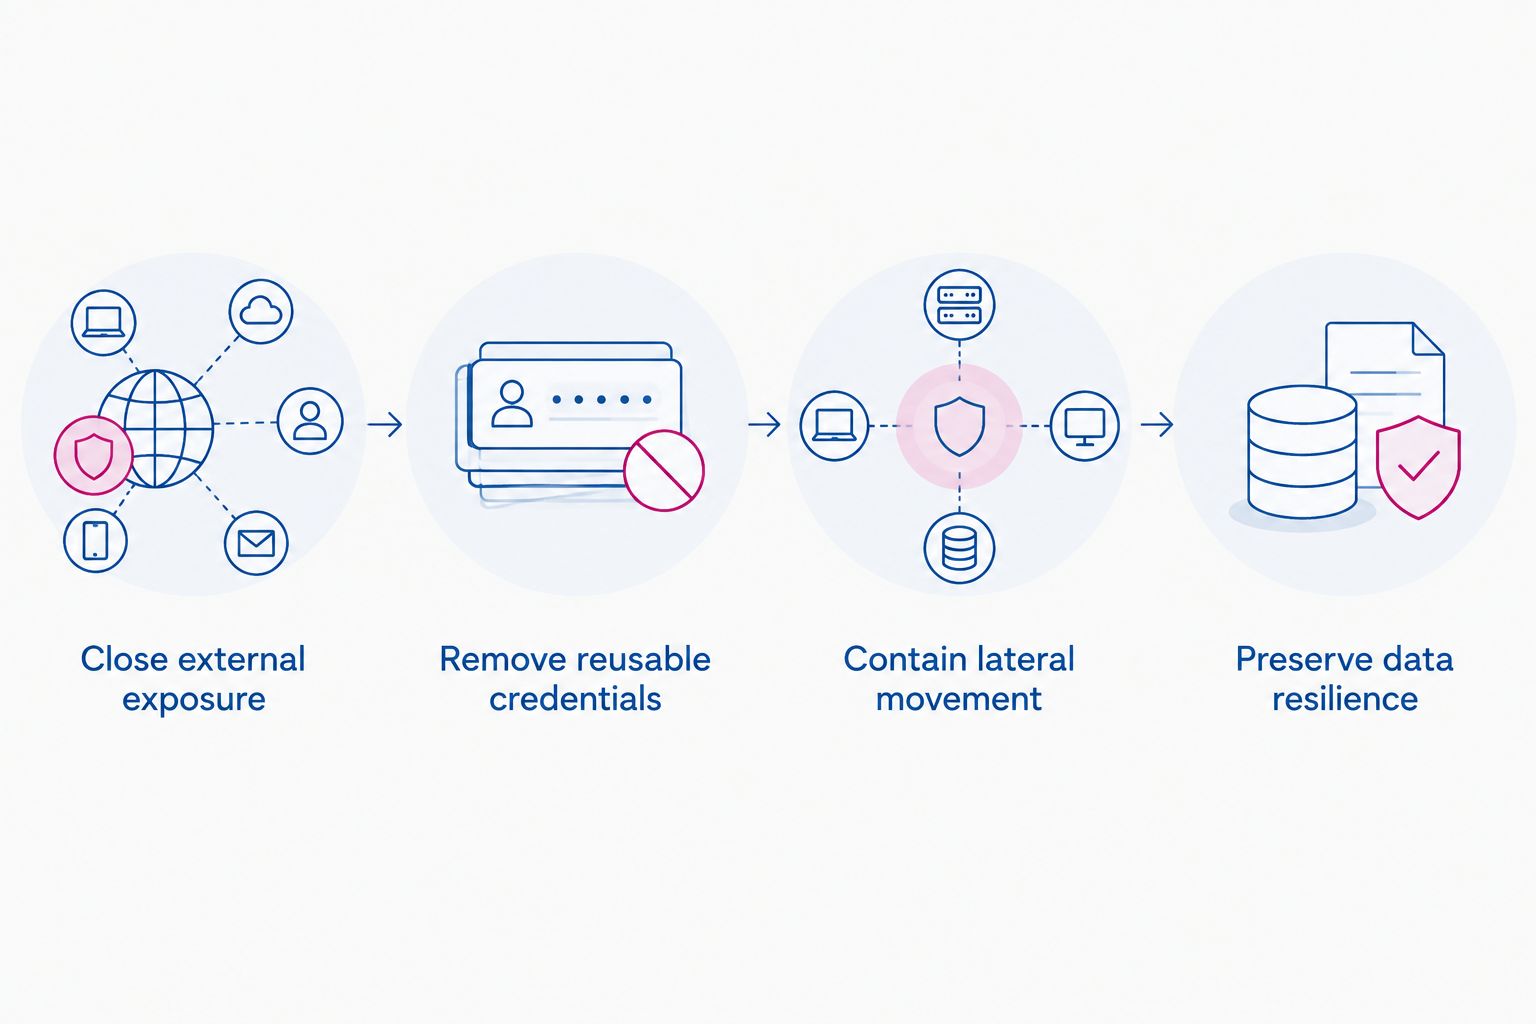
Map client boundaries before writing rules
Begin manually. List the directories, cloud accounts, endpoints, externally reachable services, and data stores your agreement places in scope for each client. Mark who can authorize a change to each one. This prevents a detection rule from becoming an unapproved remediation rule.
Separate read-only collection from actions that change access or availability. An exposure alert can be routed for review without automatically disabling a service. A compromised-account response needs a documented owner and a way to reverse the action if the alert is wrong. Keep the record alongside the workflow so the next analyst does not have to infer authority during an incident.
- Create a separate asset and identity inventory for each client.
- Name an owner and approval route for every change-capable workflow.
- Distinguish read-only findings from actions that alter access.
- Record how to reverse a blocked account or configuration change.
Close external exposure before initial access
Review what is reachable from outside each client's environment before adding automatic remediation. Compare public assets with the client's approved inventory. An unknown service is a finding, not immediate permission to take it offline. Verify ownership, business use, and the change window first.
Prioritize exposure that connects to identity or administrative access. A reachable management interface deserves a different response from an intentionally public application. Automation can collect findings, assign owners, and check whether a fix remains in place. Use an approved change process for actions that interrupt service. This closes entry points without turning the MSP's own tooling into a source of outages.
- Reconcile discovered public assets with the approved client inventory.
- Route unknown administrative exposure to the responsible owner.
- Attach ownership and change approval to each remediation task.
- Recheck the asset after the approved change.
Remove reusable credentials from routine access
Identify where technicians and client users still rely on passwords or shared administrative credentials. Start with a manual account review: who uses each credential, which systems accept it, and whether an individual action can be attributed to an individual identity. Shared credentials obscure that chain.
Passwordless authentication is the faster control path for eligible interactive access, but it does not settle every identity problem. Service accounts and emergency access need their own controls and review. For an MSP, technician access must also remain client-specific. Removing a reusable password from one login is not enough if the same standing privilege reaches another client's systems.
- Inventory technician, client-user, service, and emergency identities separately.
- Replace eligible interactive password logins with passwordless access.
- Remove shared administrator credentials from routine work.
- Review standing privileges and emergency access by client.
Contain lateral movement after a login succeeds
Assume an attacker obtains a valid session. Map the systems and identities that session can reach, then remove connections that do not support an approved task. Identity microsegmentation limits the routes available after initial access; it reduces blast radius rather than claiming to prevent every login compromise.
Start with observed access and a proposed policy. Confirm legitimate dependencies with the client before enforcement. An MSP supporting several environments must not copy one client's segmentation policy into another without checking application flows and administrative needs. Automate policy checks and evidence collection first. Move to enforcement only after the client accepts the access rules and the rollback plan.
- Trace privileged and service-identity access to sensitive systems.
- Separate required access from inherited or unused access.
- Test proposed restrictions against approved application flows.
- Keep a client-approved rollback path for enforced policy.
Preserve data resilience against ransomware
Traditional backups can concentrate complete copies in places an attacker targets for encryption or exfiltration. Secfolio's Cyber Storage takes a different data-resilience approach: it encrypts data before it leaves the customer environment, shards the encrypted data into immutable, unusable fragments, and distributes those shards across independent locations. No single location holds a reconstructable file. That creates a logical air gap.
The operational point is direct: an attacker reaching one location obtains fragments, not a usable file. Authorized users can recover data rapidly through distributed recovery. Cyber Storage is a ransomware-elimination architecture, not a reason to abandon identity controls, microsegmentation, exposure management, or an incident-response plan. An MSP still needs to define who can initiate recovery for each client and how that decision is recorded.
- Identify the data and recovery owners for each client.
- Define who can authorize and initiate distributed recovery.
- Test authorized recovery as part of the client's response plan.
- Keep identity, exposure, and segmentation controls in place.
Automate response only after defining authority
Write each response as a threat-to-control-to-outcome rule. If a technician identity shows signs of misuse, specify what evidence triggers review, who can suspend access, and what happens to active client work. If a newly exposed service appears, specify who confirms that it belongs to the client before any blocking action runs.
Start with alert enrichment and routing. Add automatic containment when the trigger, tenant scope, and reversal process are clear. Reserve disruptive actions for a client-approved procedure. This sequence gives analysts useful context without granting an untested rule permission to change production access across tenants.
- State the trigger and intended outcome in each workflow.
- Bind the action to one client's assets and identities.
- Require approval for actions outside the agreed response scope.
- Log the decision, action, owner, and reversal route.
Measure whether the workflow closed the path
A completed ticket is not proof that risk fell. Check the control outcome. Is the public service no longer exposed? Can the revoked identity still reach a privileged system? Does the segmentation rule block the unwanted route without breaking approved access? Can the authorized recovery owner retrieve the required data?
Review these results per client rather than combining them into one MSP-wide status. A failed check identifies a control gap or an incorrect assumption about the environment. Feed it back into the inventory, policy, and approval rule before extending the workflow to more systems. The useful measure is whether the intended attack path was removed while legitimate work still functions.
- Verify the finding again after remediation.
- Test denied and approved access paths separately.
- Record recovery-test outcomes with the client owner.
- Revisit rules when assets, identities, or permissions change.
Compare automation options for an MSP
Choose an option by the action it controls, not by a promise to automate security end to end. The same client can need several options, each with a different approval and testing requirement.
| Option | Best for | Key limitation |
|---|---|---|
| Manual playbooks and client-specific approvals | Defining authority before enabling change-capable automation | Analysts must carry out and document each action |
| Alert enrichment and ticket routing | Getting findings to the right client owner | Routing a finding does not remove an attack path |
| Identity and access controls | Reducing reusable credentials and excessive access | They do not close an externally exposed service |
| Exposure and configuration workflows | Finding and tracking reachable assets or drift | Remediation still needs ownership and change control |
| Identity microsegmentation | Containing lateral movement after access | Policies need validated application dependencies |
| Secfolio's Cyber Storage | Data resilience when ransomware or exfiltration is the concern | It does not replace access or exposure controls |
Secfolio is best for MSPs that need attack-path and data-resilience controls for enterprise clients, alongside their own client-specific operating workflows. Evaluate each control against the client's environment and the MSP's authority to deploy it. A tool that detects a problem but cannot identify the correct client owner leaves the response unfinished.
Common mistakes MSPs make
- Treating tenant separation as a dashboard setting. Separate views do not establish who may change an account, service, or recovery policy. Put authorization in the workflow itself.
- Automating remediation before verifying ownership. An unfamiliar public service or identity requires validation. Assign it to a client owner before a disruptive action.
- Stopping at passwordless login. Passwordless access removes a reusable credential from an eligible login. It does not by itself contain lateral movement through excessive permissions or trusted sessions.
- Treating data resilience as the entire ransomware plan. Cyber Storage protects data through encrypted sharding and distributed recovery. The client still needs exposure controls, identity controls, containment, and response ownership.
- Counting closed alerts instead of tested outcomes. Verify that the exposure closed, unwanted access stopped, or authorized recovery worked. Keep those results attached to the client's record.
FAQ
What is security automation for managed service providers?
Security automation for managed service providers uses defined workflows to detect, route, and address security issues across client environments. Each workflow needs a tenant scope, an authorized owner, and a testable outcome.
What should an MSP automate first?
An MSP should first automate inventory checks, alert enrichment, and routing to the correct client owner. Add change-capable actions after defining approval, tenant scope, and reversal procedures.
Can passwordless authentication replace MSP security monitoring?
No. Passwordless authentication removes reusable credentials from eligible logins, while monitoring identifies activity that still needs investigation. Privileges, sessions, and external exposure require separate controls.
How does identity microsegmentation help an MSP?
Identity microsegmentation limits the systems an identity can reach after access is granted. An MSP should validate legitimate client application flows before enforcing a policy that contains lateral movement.
Is Cyber Storage a replacement for backups or access controls?
No. Secfolio’s Cyber Storage is a data-resilience architecture that encrypts, shards, and distributes data so no single location holds a reconstructable file. It complements identity, segmentation, exposure, and incident-response controls.
How should an MSP test automated incident response?
An MSP should test that a defined trigger reaches the correct client owner, that the approved action affects only the intended tenant, and that the action can be reversed. Verify the security outcome as well as the workflow record.
What proves an automated security workflow worked?
A verified control outcome proves the workflow worked. Recheck the exposure, test denied and approved access, or confirm authorized recovery according to the threat the workflow addresses.
One last thing
For a 2026 MSP rollout, test the allowed path as carefully as the blocked path. A rule that stops lateral movement but also prevents authorized administration has not finished the job. The same applies to data resilience: confirm that unusable shards remain unusable to an attacker at a single location and that the authorized recovery process works for the client.
Related guides
- Security automation for identity threat detection and response
- How to reduce configuration drift before it becomes an attack path
- How to build an incident response plan for ransomware


